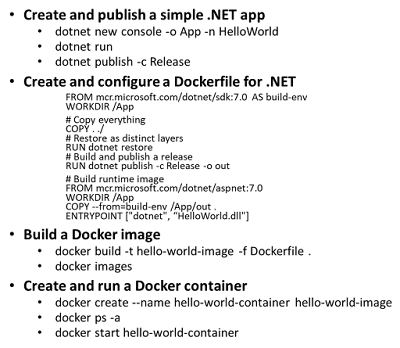
Prerequisites

Sitecore exposes /identity/externallogincallback URL which basically invokes the HandleLoginLink processor whose primary responsibility is to transfer the AspNet.ExternalCookie issued by OIDC in to final AspNet.Cookies authentication token. The sitecore virtual users then get created and session is initialized. Therefore we must include the above end point as our callback end point. Once this callback is triggered, it will redirect the user to returnUrl specified.
https://stackoverflow.com/questions/29907155/external-cookie-for-external-login-in-asp-net-owin
https://blog.baslijten.com/federated-authentication-in-sitecore-error-unsuccessful-login-with-external-provider
Technically this is what it does behind the scene- This is just a hack , don't use this. Refer above code snippet to redirect to Sitecore external call back to get away with External Cookie reference.App Registrations
Select Policy
|
Scale In /Out |
Scale Up/Down |
|
Downtime: No downtime when provisioning in
cloud |
Downtime to some extent as there will be migration
of code and configuration. No downtime when scaling process happens however
migration of code configuration kicks off post scaling results in downtime. |
|
Scenario: When code is alright, however no of users
during the peak increases and server is unable to serve request. Increase no
of boxes or instance to distribute loads of users across . Load balancing of
users or distribution of users to serve request. |
Scenario : When bad code or design leads to more
CPU and memory utilizations. Need to increase server capacity |
|
No sticky session Out proc session |
In Proc session or state server session will do. |
|
|
|
Clusters| Nodes| Pods| Helm
Node := Master Node + No. of Worker Nodes
Analogy: Cluster is like a train and Nodes are just like a compartment

Kubernetes clusters are comprised of one master node and a number of worker nodes. These nodes can either be physical computers or virtual machines, depending on the cluster. The master node controls the state of the cluster; for example, which applications are running and their corresponding container images.


CSP protect from XSS
Well if you are working on .Net the only option you have is to add custom response header in Web.config file and list all JS. But here is the catch if you working with third party analytics this become tricky. There is a constraint and challenge to do so. Per say, these analytics injects lot of js libraries at runtime. It can be facebook , google tag manager, live person, social media plugins or advert. This is where one needs to draw line and give business technical reason why this cannot be achieved. Next stuff is browser compatibility. Under the hood testing will become exhaustive and chances are these are prones to more defects that leads to unknowns while move to production. Next time you come across CSP , think twice do your thorough research before you commit something.
Remote name could not be resolved 'dist.nuget.org'
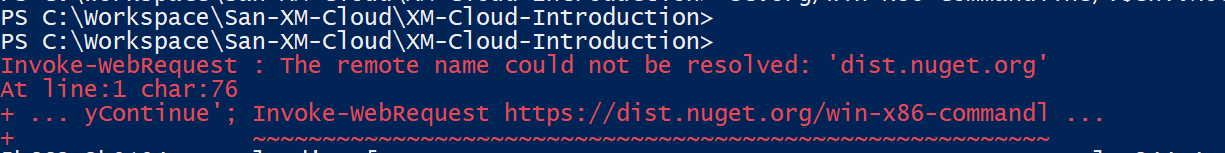

Next, set the Interface Metric to 1 for Wi-Fi
Set-NetIPInterface -InterfaceAlias 'Wi-Fi' -InterfaceMetric 1
https://sitecore.stackexchange.com/questions/26095/remote-name-could-not-be-resolved-dist-nuget-org
I started with Github repo and followed the step. I got error while running the step given below
Next, use the up.ps1 script to bring up all of the containers required for Local Mode.
.\up.ps1ERRORa Windows version 10.0.20348-based image is incompatible with a 10.0.19042 hostI refer version of docker https://hub.docker.com/_/microsoft-dotnet-sdkGo to .env file and change this configuration FROMNETCORE_BUILD_IMAGE=mcr.microsoft.com/dotnet/sdk:6.0-nanoserver-ltsc2022
NETCORE_RELEASE_IMAGE= mcr.microsoft.com/dotnet/aspnet:6.0-nanoserver-ltsc2022TONETCORE_BUILD_IMAGE=mcr.microsoft.com/dotnet/sdk:6.0.400-nanoserver-1809
NETCORE_RELEASE_IMAGE= mcr.microsoft.com/dotnet/aspnet:6.0.400-nanoserver-1809
Friendly reminder about C# expression-bodied methods 🙂🙏 #dotnet pic.twitter.com/XnUAnmOdQr
— Dan Clarke 🎙 (@dracan) July 19, 2022
C#: String.IsNullOrEmpty vs String.IsNullOrWhiteSpace
🌊 C#: String.IsNullOrEmpty vs String.IsNullOrWhiteSpace 🌊
— Davide Bellone 🐧 (@BelloneDavide) July 20, 2022
What happens to your validation if the user enters a string like " "? That string is made of white spaces, so it is not empty.
Consider using IsNullOrWhiteSpace when validating inputs!#csharp #dotnet pic.twitter.com/s7jSsjCHlh
#100DaysOfCode
— san (@santoshpoojari3) August 19, 2021
Csharp Best practice - Const pic.twitter.com/bESVIrbfR3
Download https://msbuildlog.com/

Visual Studio Build Log Extension
Tools to make working with the Visual Studio project system for C#, Visual Basic, and F# easier. This extension is for VS2017 and VS2019. Search the extension marketplace if you require a different version. Build loggingA tool window is added under See the docs for more information. |
https://marketplace.visualstudio.com/items?itemName=VisualStudioProductTeam.ProjectSystemTools
Next time you write Hello World! Do this,
Clean code always looks like it was written by someone who cares.”
― Robert C. Martin, Uncle Bob
C# Exception filters has been around since advent of C# 6.0 , I'm sure we rarely use it because we are so used to old way of using conditional exception handling.
Cut to the chase........!
Run dotnet in browser
https://try.dot.net/


Happy Coding!
Managed Identities are in essence 100% identical in functionality and use case than Service Principals. In fact, they are actually Service Principals.
What makes them different though, is: – They are always linked to an Azure Resource, not to an application or 3rd party connector – They are automatically created for you, including the credentials; big benefit here is that no one knows the credentials
Managed Identities exist in 2 formats: – System assigned; in this scenario, the identity is linked to a single Azure Resource, eg a Virtual Machine, a Logic App, a Storage Account, Web App, Function,… so almost anything. Next, they also “live” with the Azure Resource, which means they get deleted when the Azure Resource gets deleted. – User Assigned Managed Identity, which means that you first have to create it as a stand-alone Azure resource by itself, after which it can be linked to multiple Azure Resources. An example here could be out of an integration with Key Vault, where different Workload services belonging to the same application stack, need to read out information from Key Vault. In this case, one could create a “read KV” Managed Identity, and link it to the web app, storage account, function, logic app,… all belonging to the same application architecture.
Let’s walk through a quick demo scenario for both, using a Virtual Machine as Azure Resource:
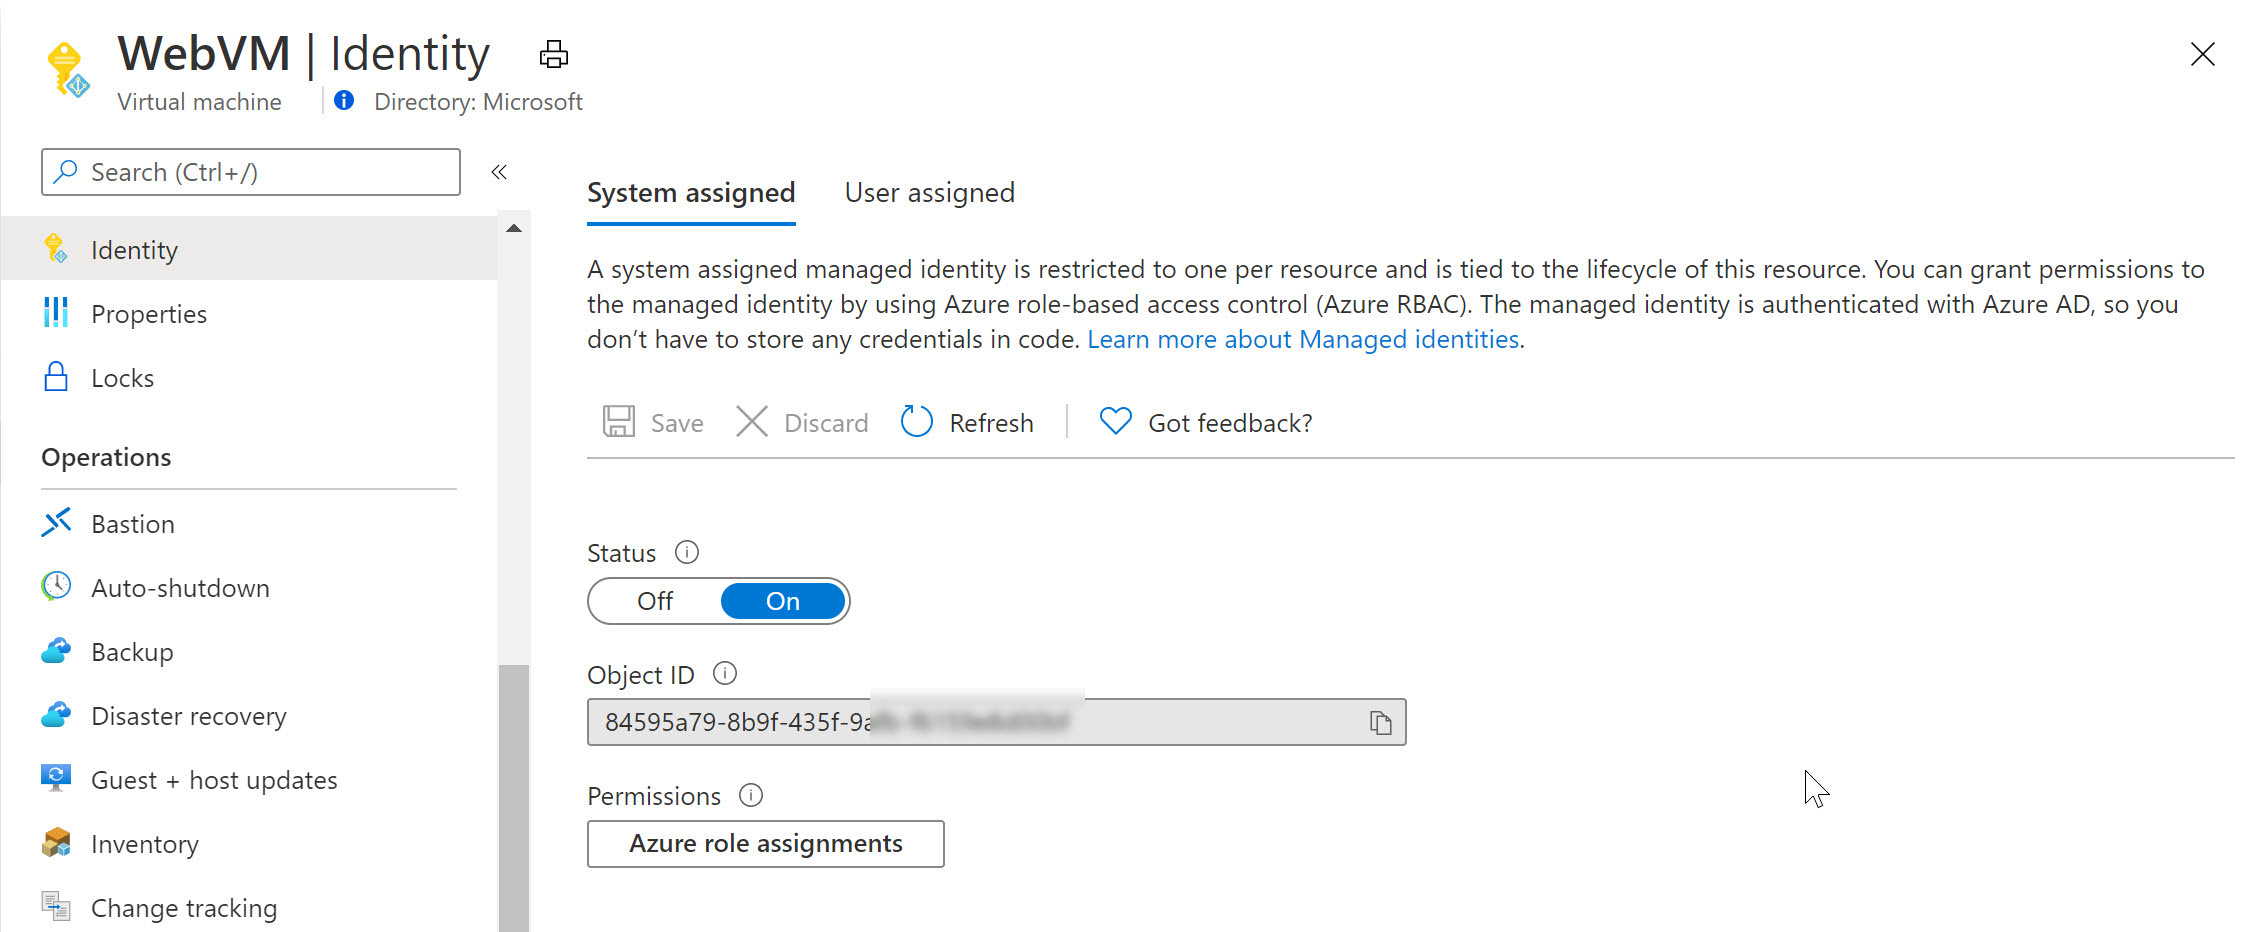
Switching to Azure Key Vault / Access Policies, we can now define this System Assigned Managed Identity having get and list permissions (or any other) for keys, secrets or certificates. For example reading out an Azure Storage Account Access key or similar.
Notice how Azure Key Vault is expecting a Service Principal object here (where in reality we are using a Managed Identity).
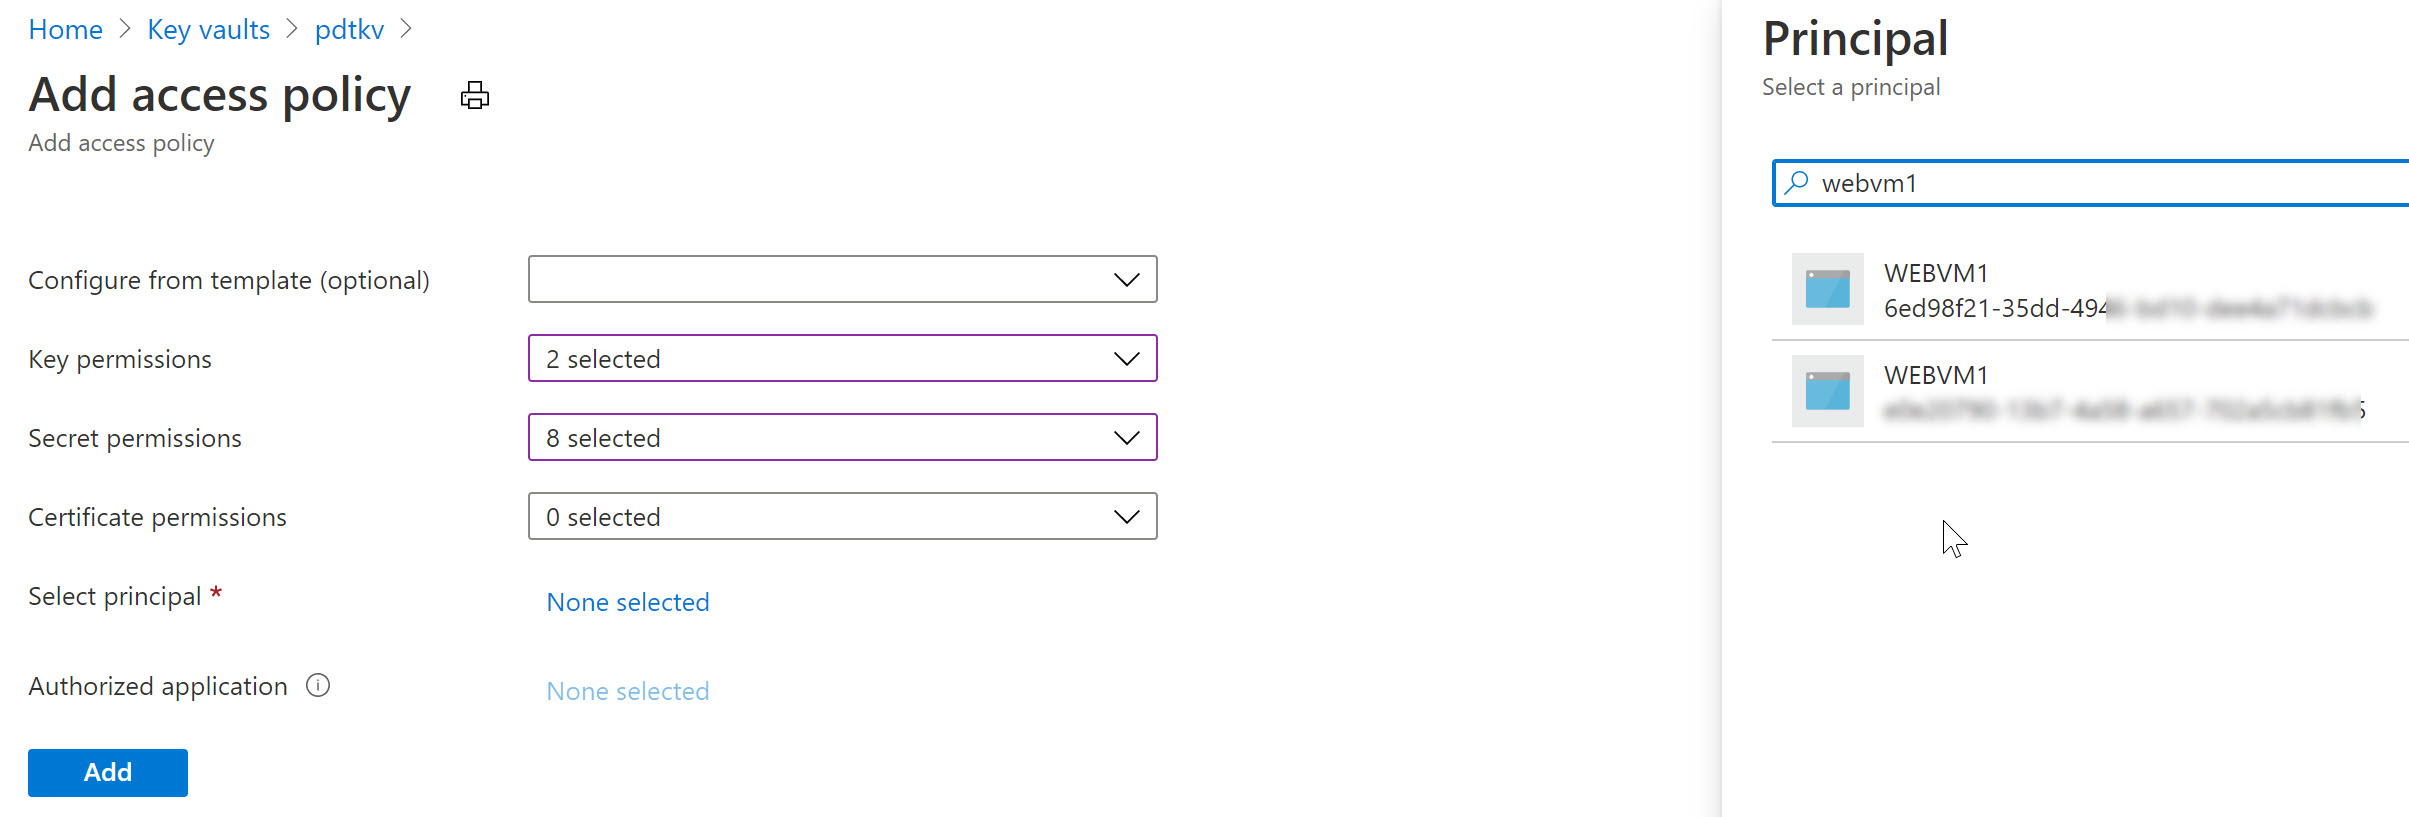
Similarly, let’s remove the System Assigned MI of the VM and use a User Assigned one in the next example (an Azure Resource can only be linked to one or the other, not both…):
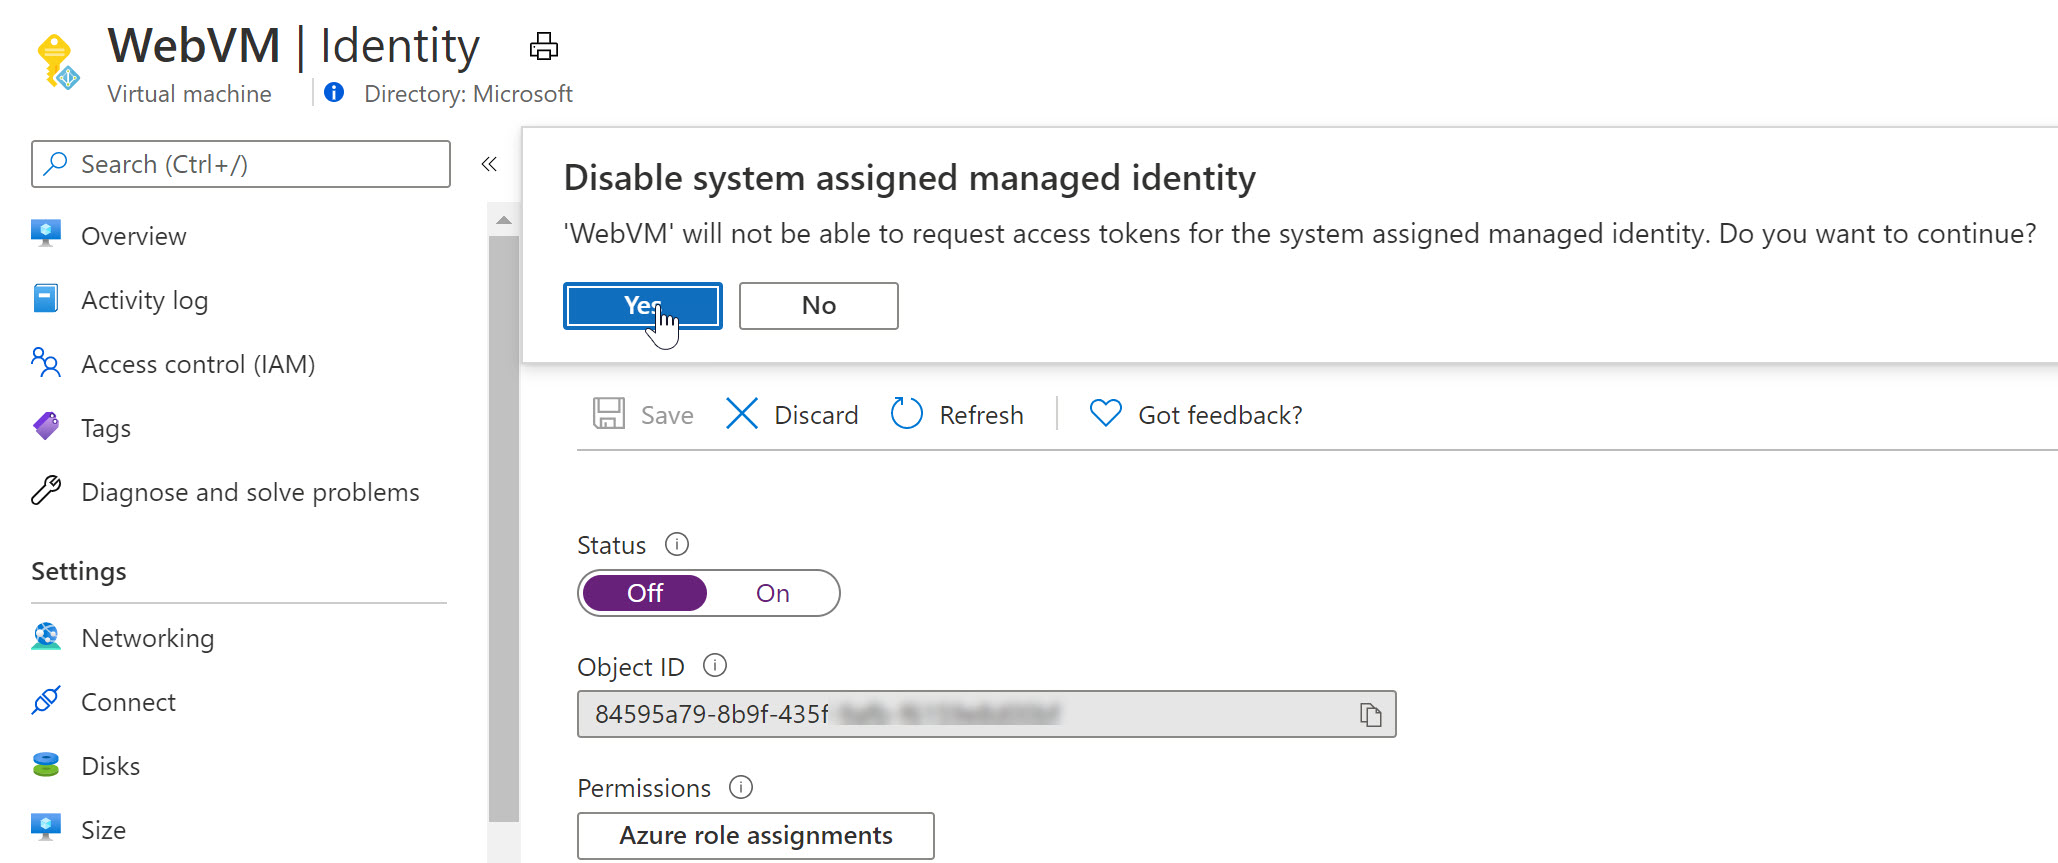
As you notice, the Managed Identity object gets immediately removed from Azure AD. Yes, security is key here…
Remember that a User Assigned Managed Identity is a stand-alone Azure Resource, which needs to be created first, after which you can assign it to another Azure Resource (our VM in this scenario).
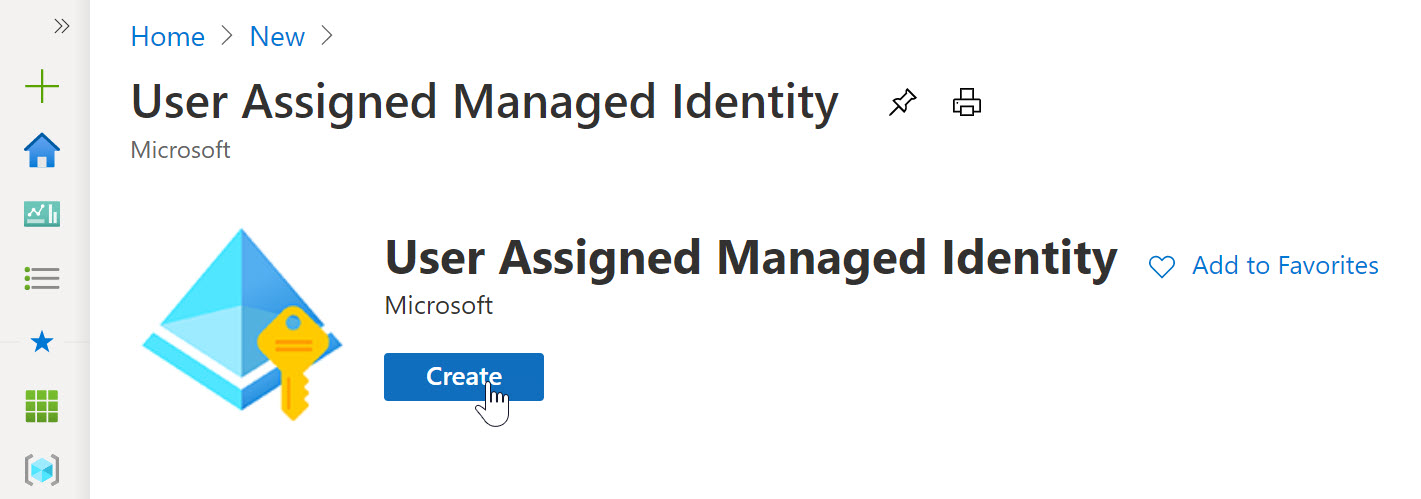
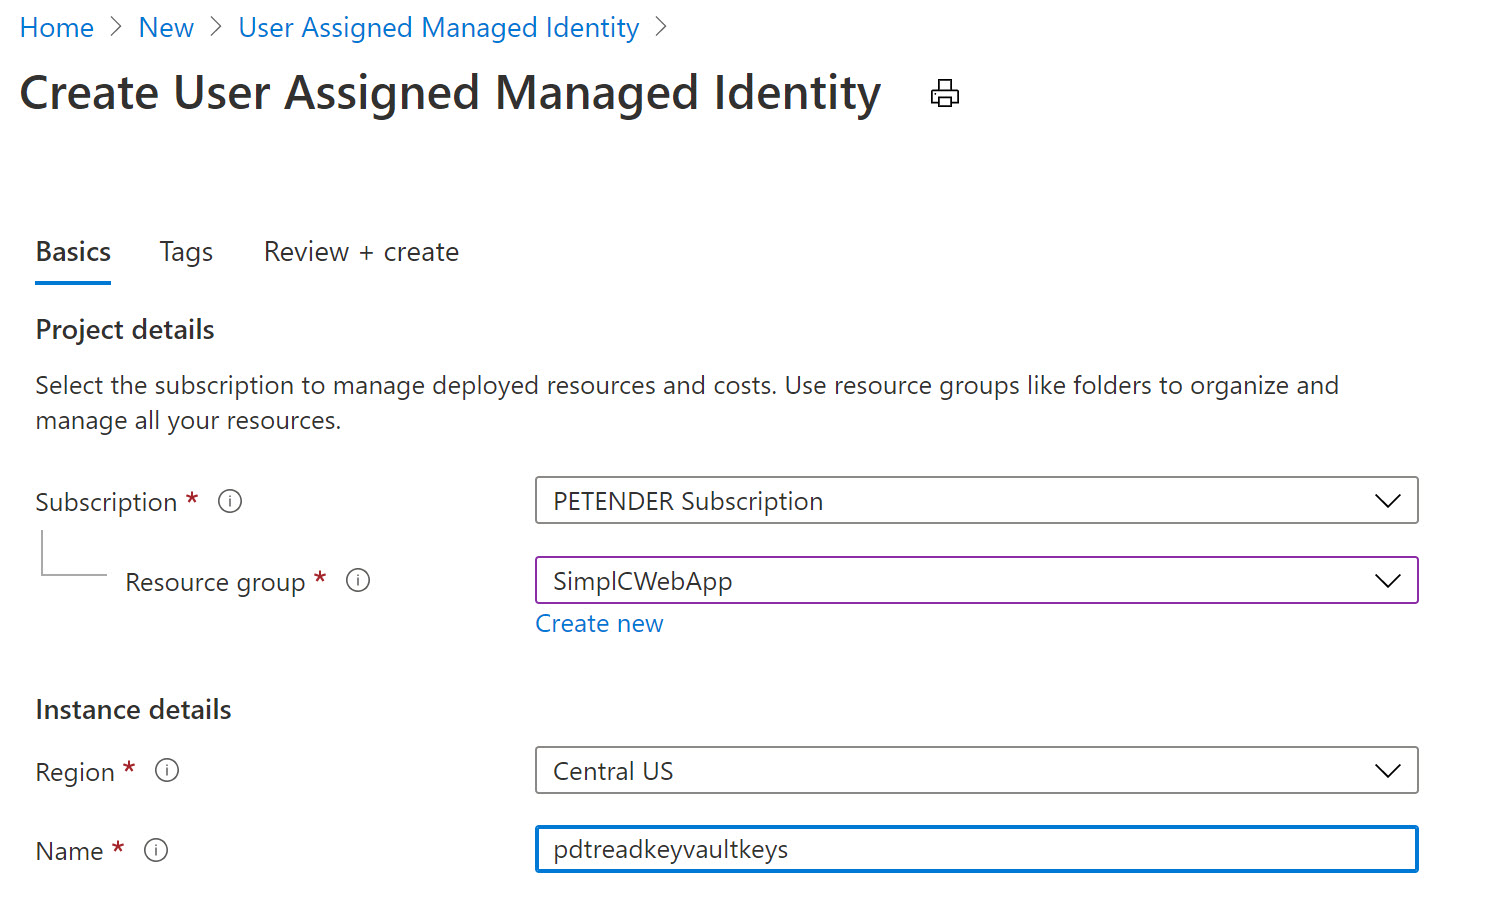
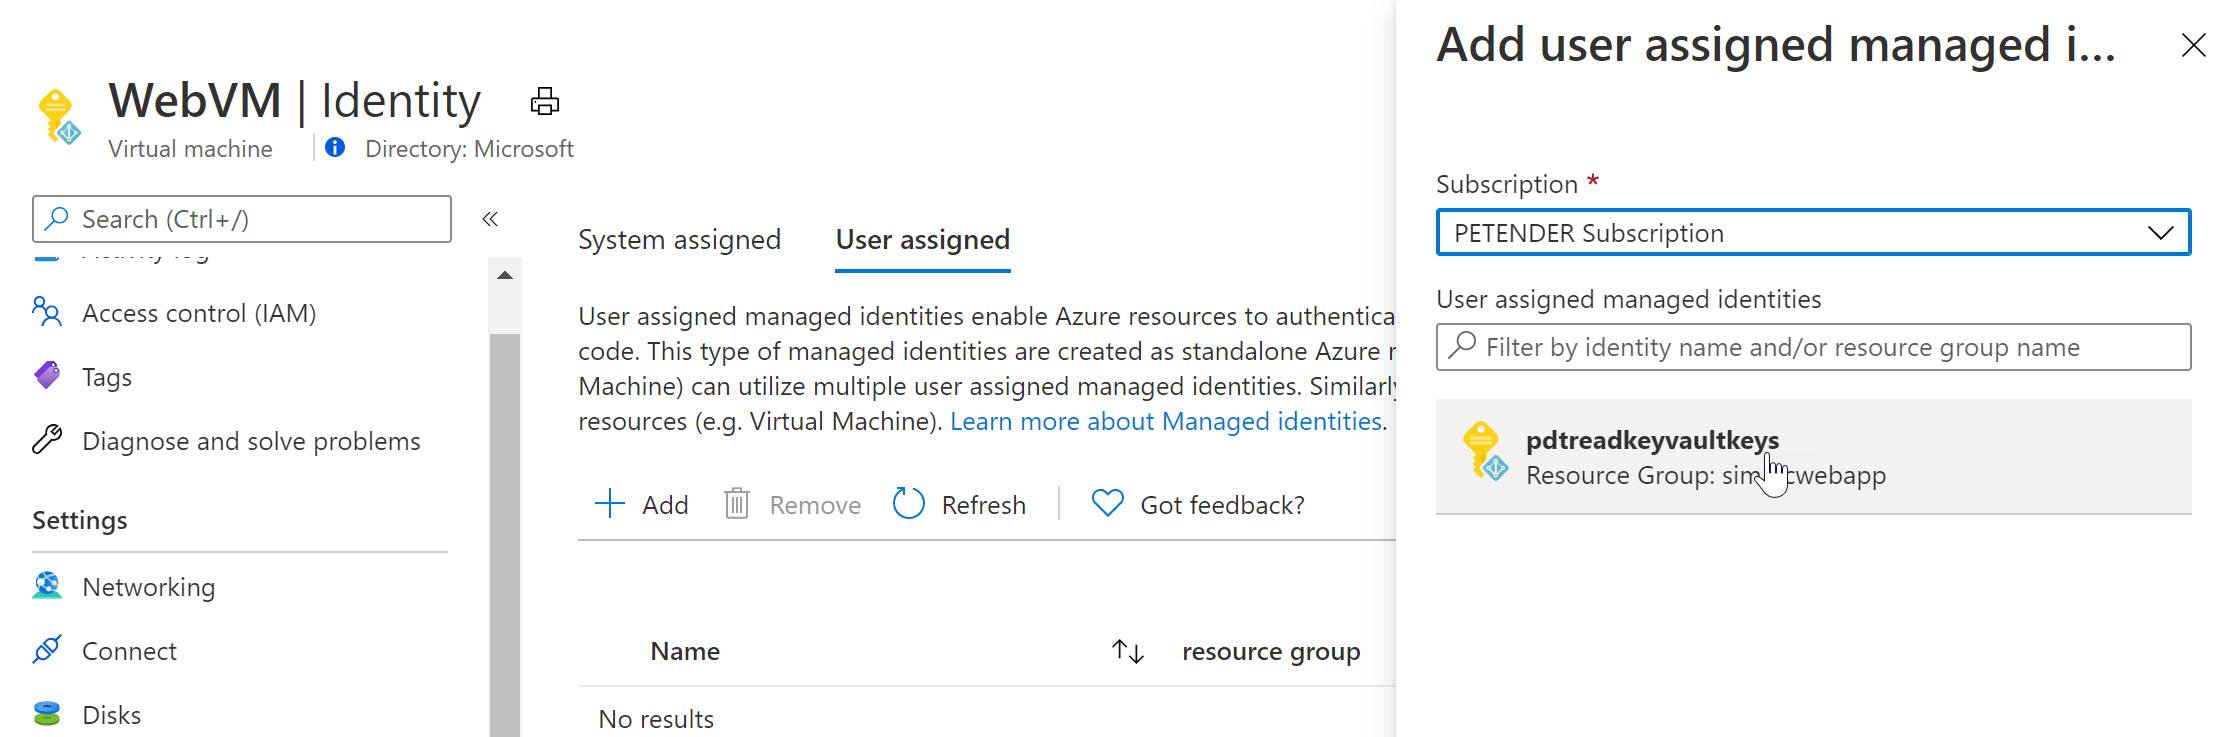
Select it and add it as a Virtual Machine User Assigned object.
Select another Azure Resource in your subscription, for example an Azure Web App, Logic App,… and once more select Identity from the settings. Below screenshot shows what it looks like for an Azure Web App Resource:
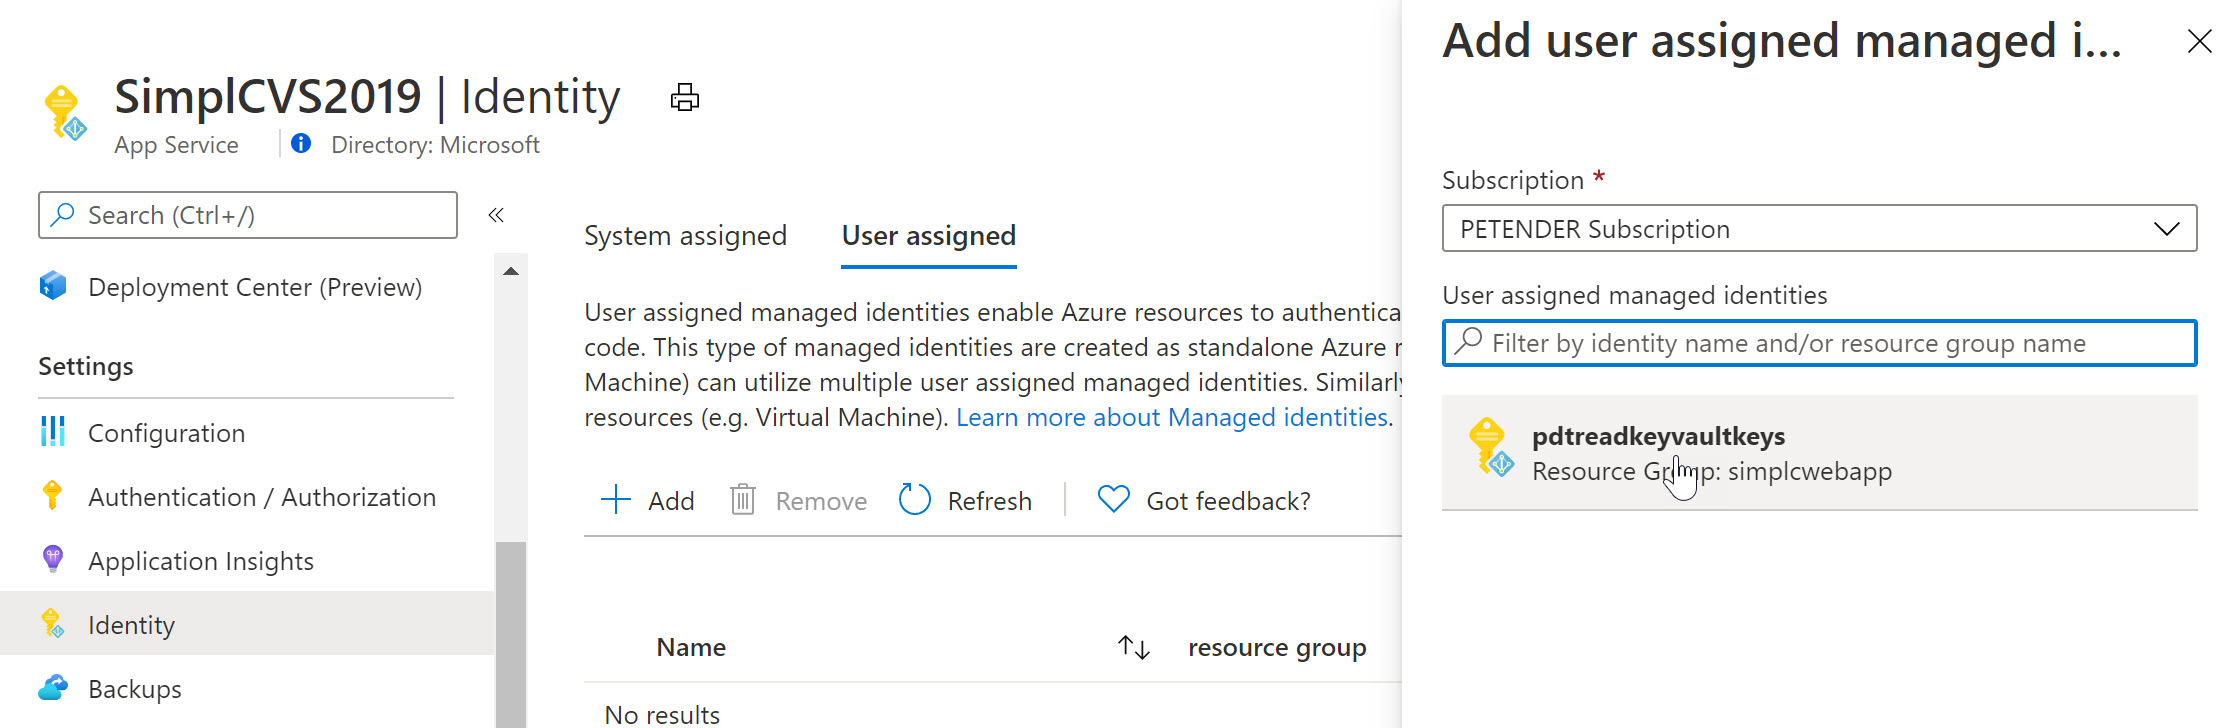
To complete the sample scenario, let’s go back to Azure Key Vault, and specify another Access Policy for this User Assigned Managed Identity:
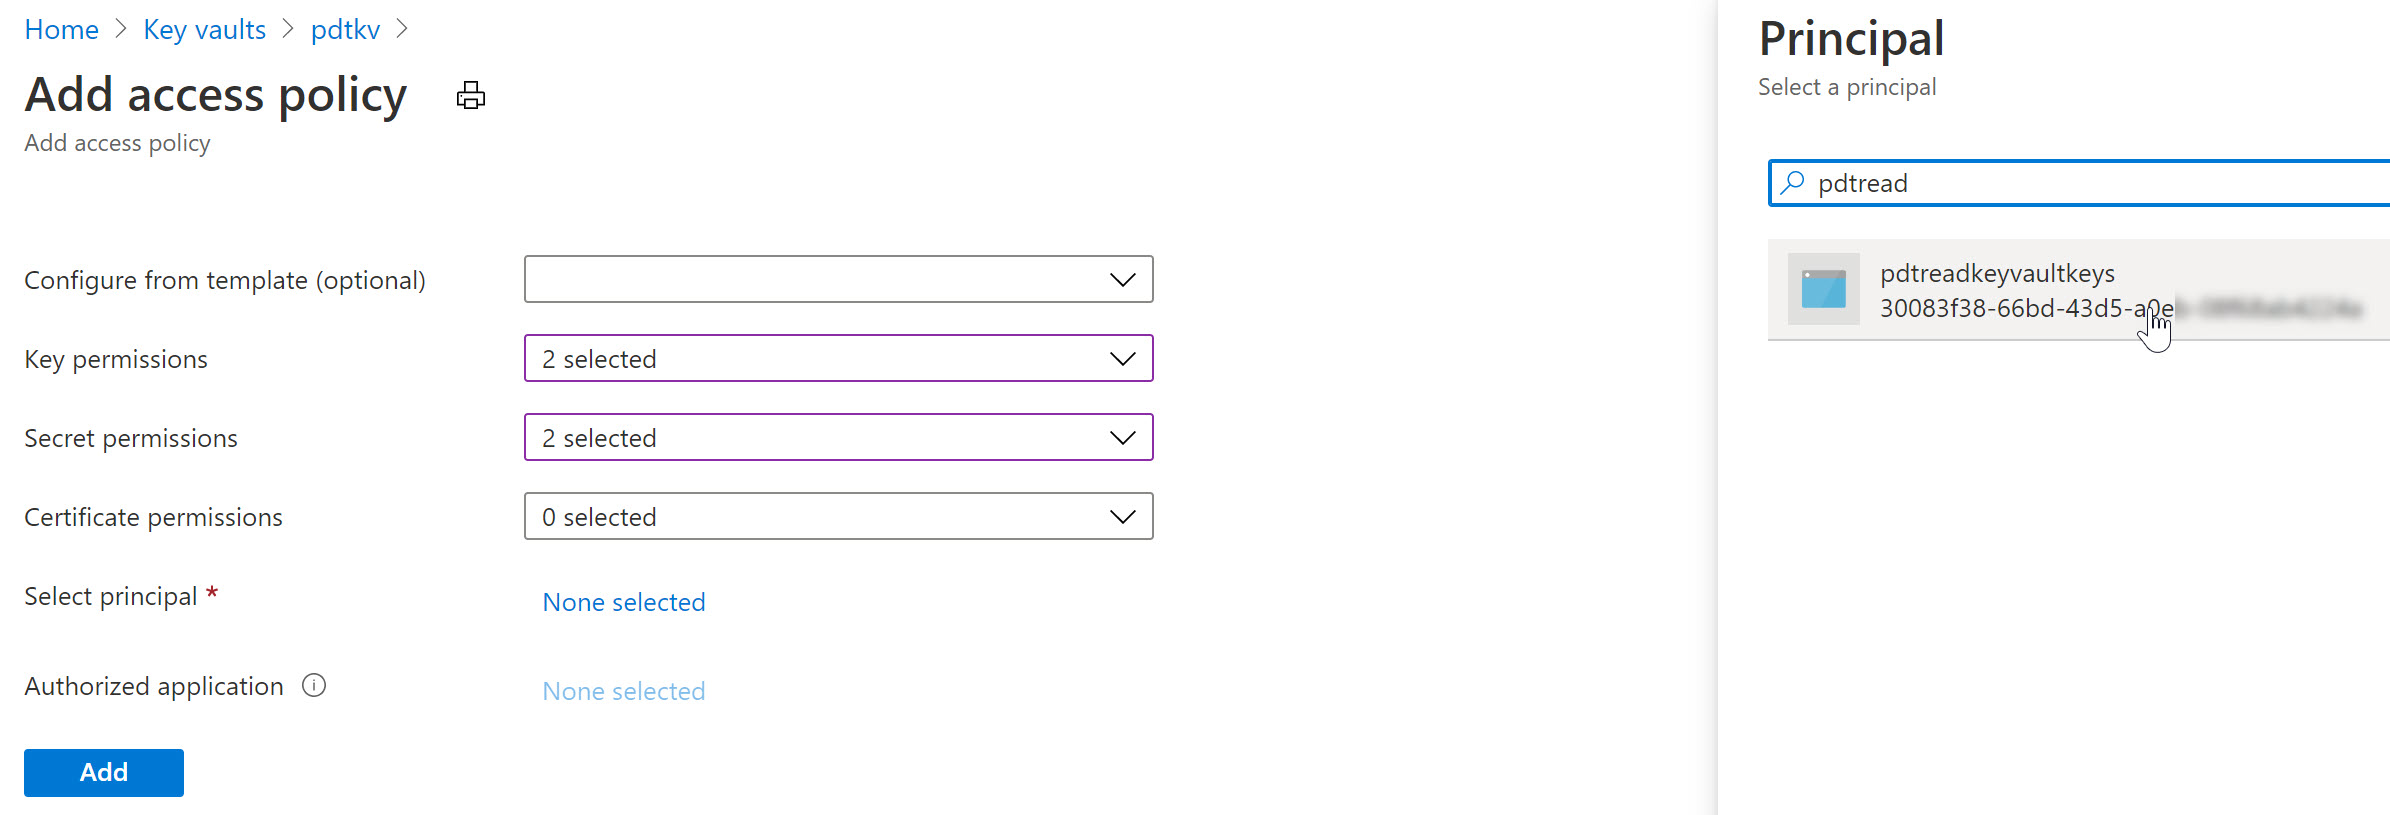
After saving the changes, the result is that now both the Azure Virtual Machine as well as the Web App – having the User Assigned Managed Identity assigned to them – can read our keys and secrets from Azure Key Vault.
In this post, I wanted to clarify the use case, difference and similarities between Service Principals and Managed Identities. A Service Principal could be looked at as similar to a service account-alike in a more traditional on-premises application or service scenario. Managed Identities are used for “linking” a Service Principal security object to an Azure Resource like a Virtual Machine, Web App, Logic App or similar. For a 1:1 relation between both, you would use a System Assigned, where for a 1:multi relation, you would use a User Assigned Managed Identity.